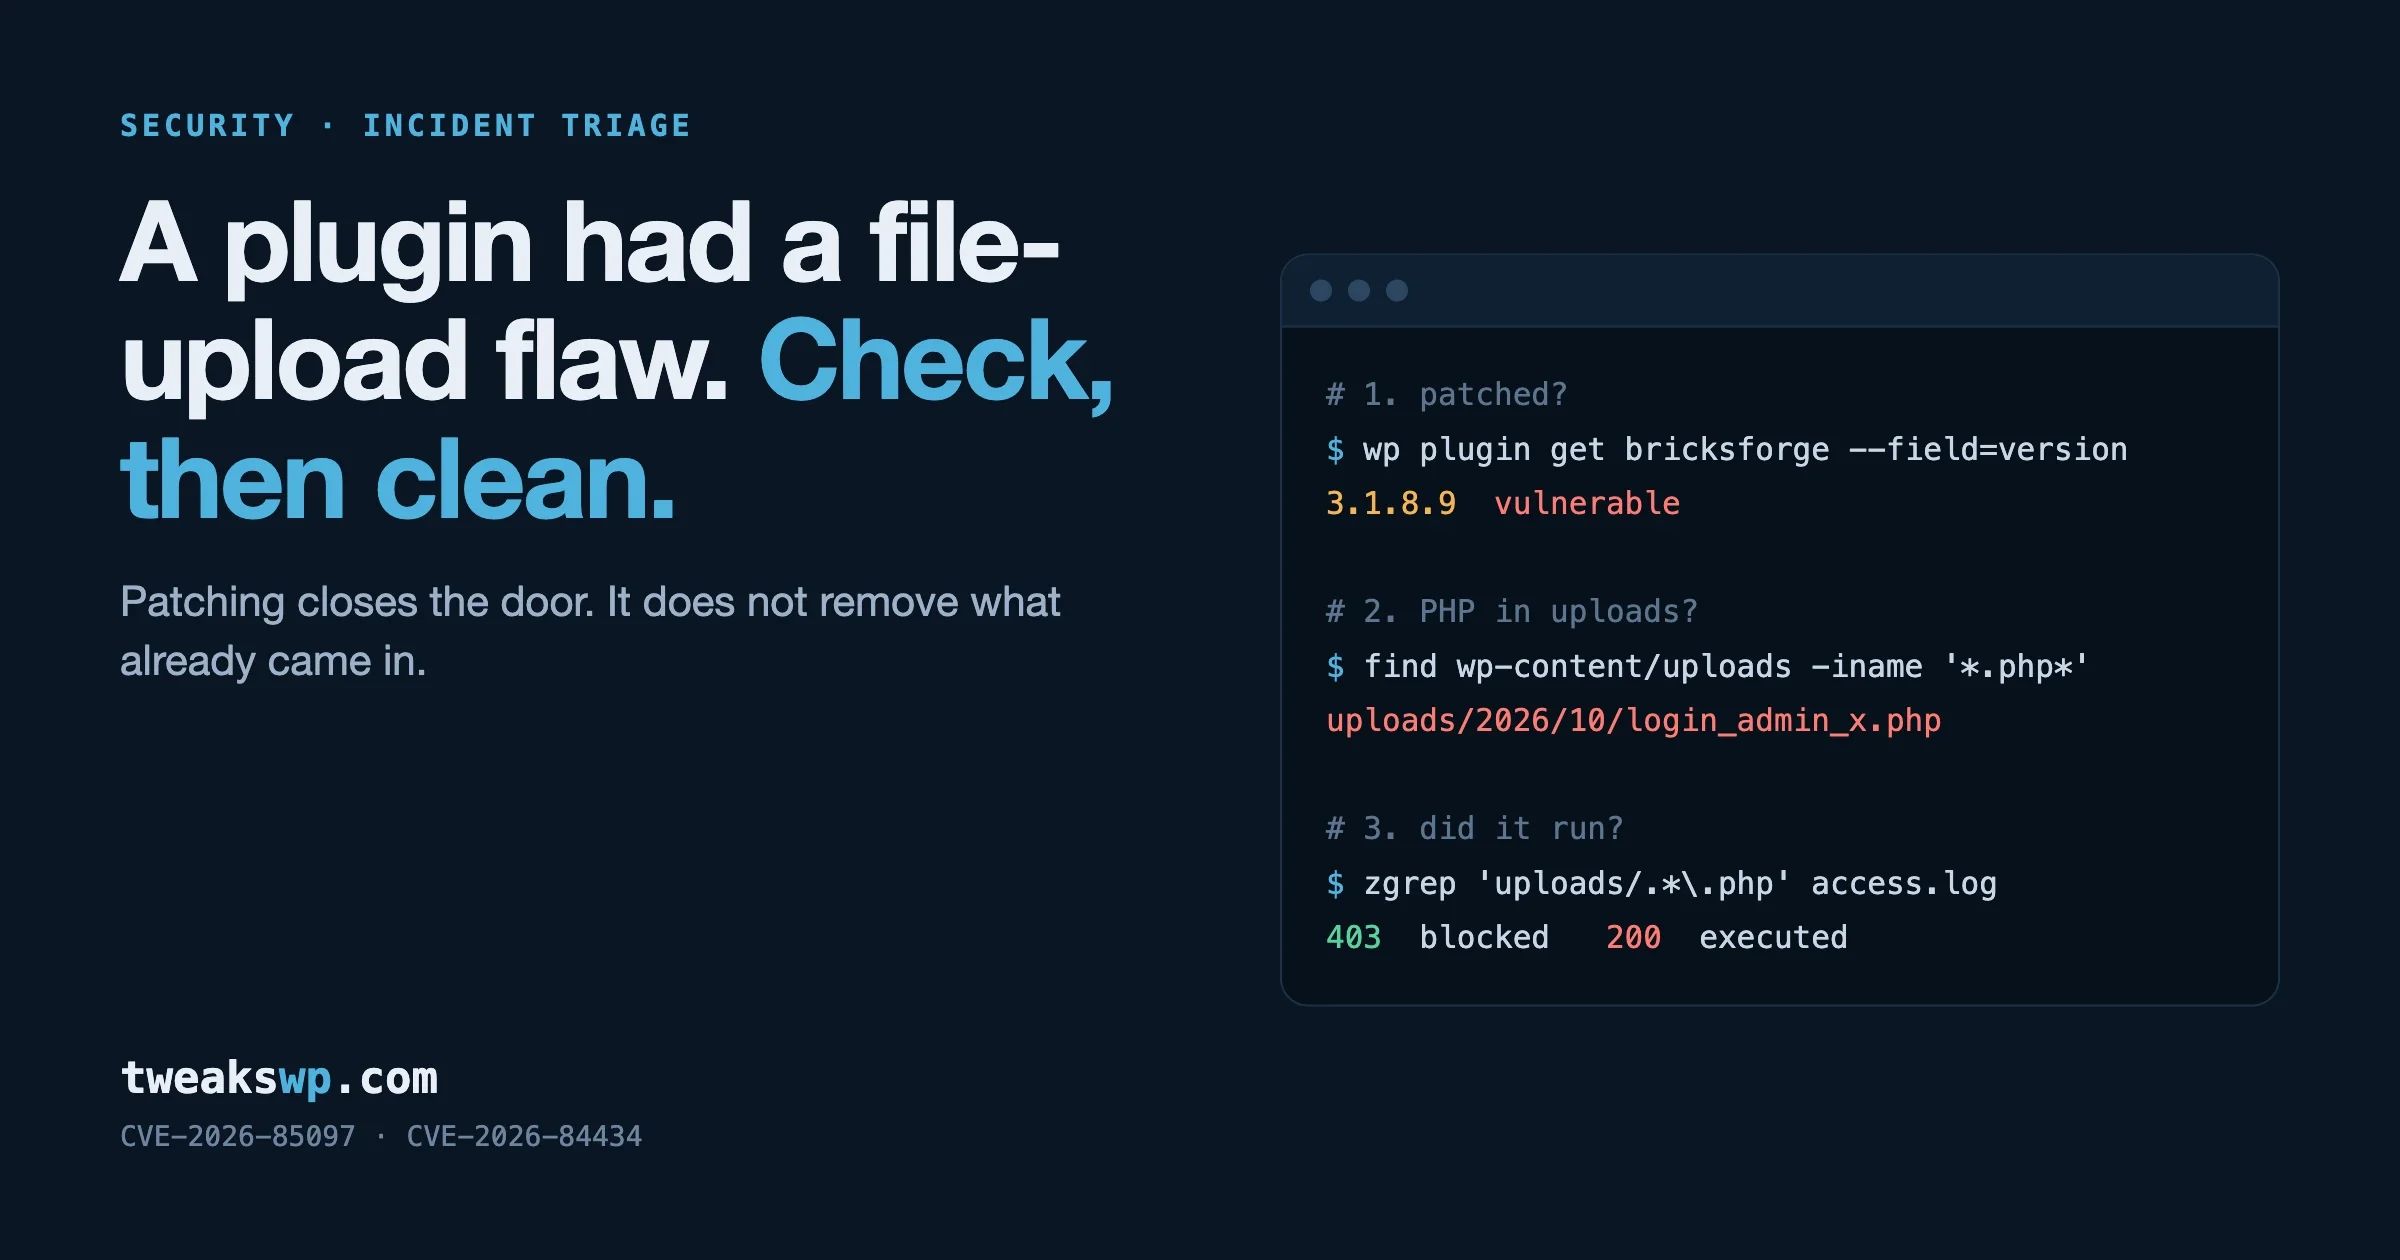
File-Upload Flaw in a Plugin: How to Check and Clean
Patching a file upload vulnerability does not remove what was uploaded. Version, uploads and log checks for Bricksforge CVE-2026-85097 and Gravity Forms.
Security9 min read
Patching a file upload vulnerability does not remove what was uploaded. Version, uploads and log checks for Bricksforge CVE-2026-85097 and Gravity Forms.
Security9 min read
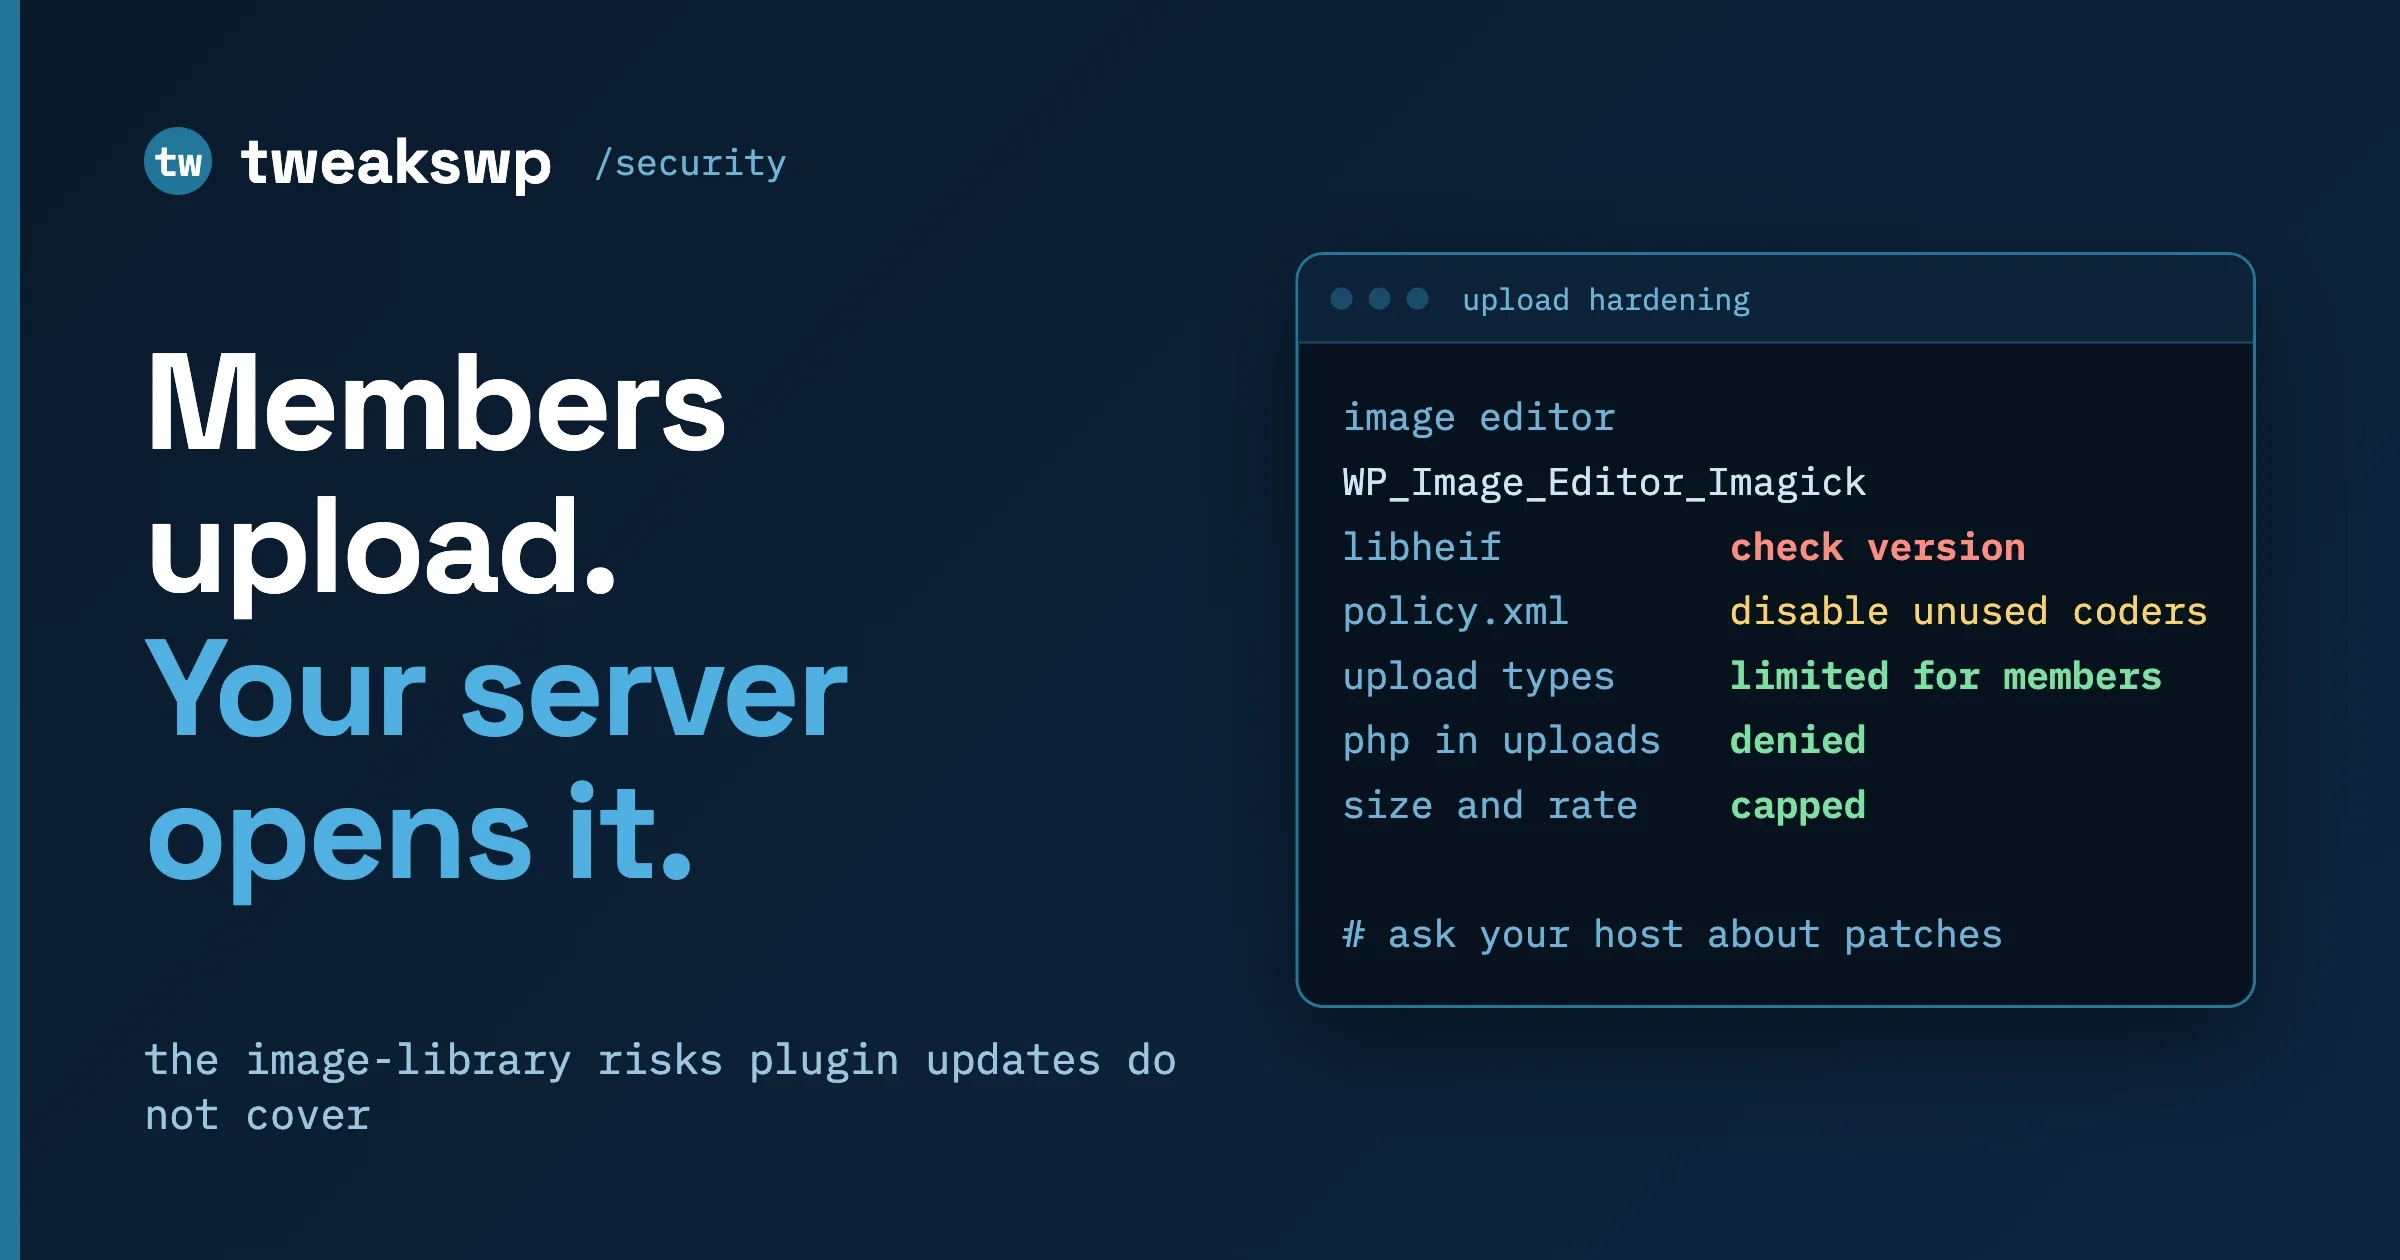
Plugin updates do not patch the image libraries your server uses. How to check your stack and harden member uploads, with libheif as the example.
Security14 min read
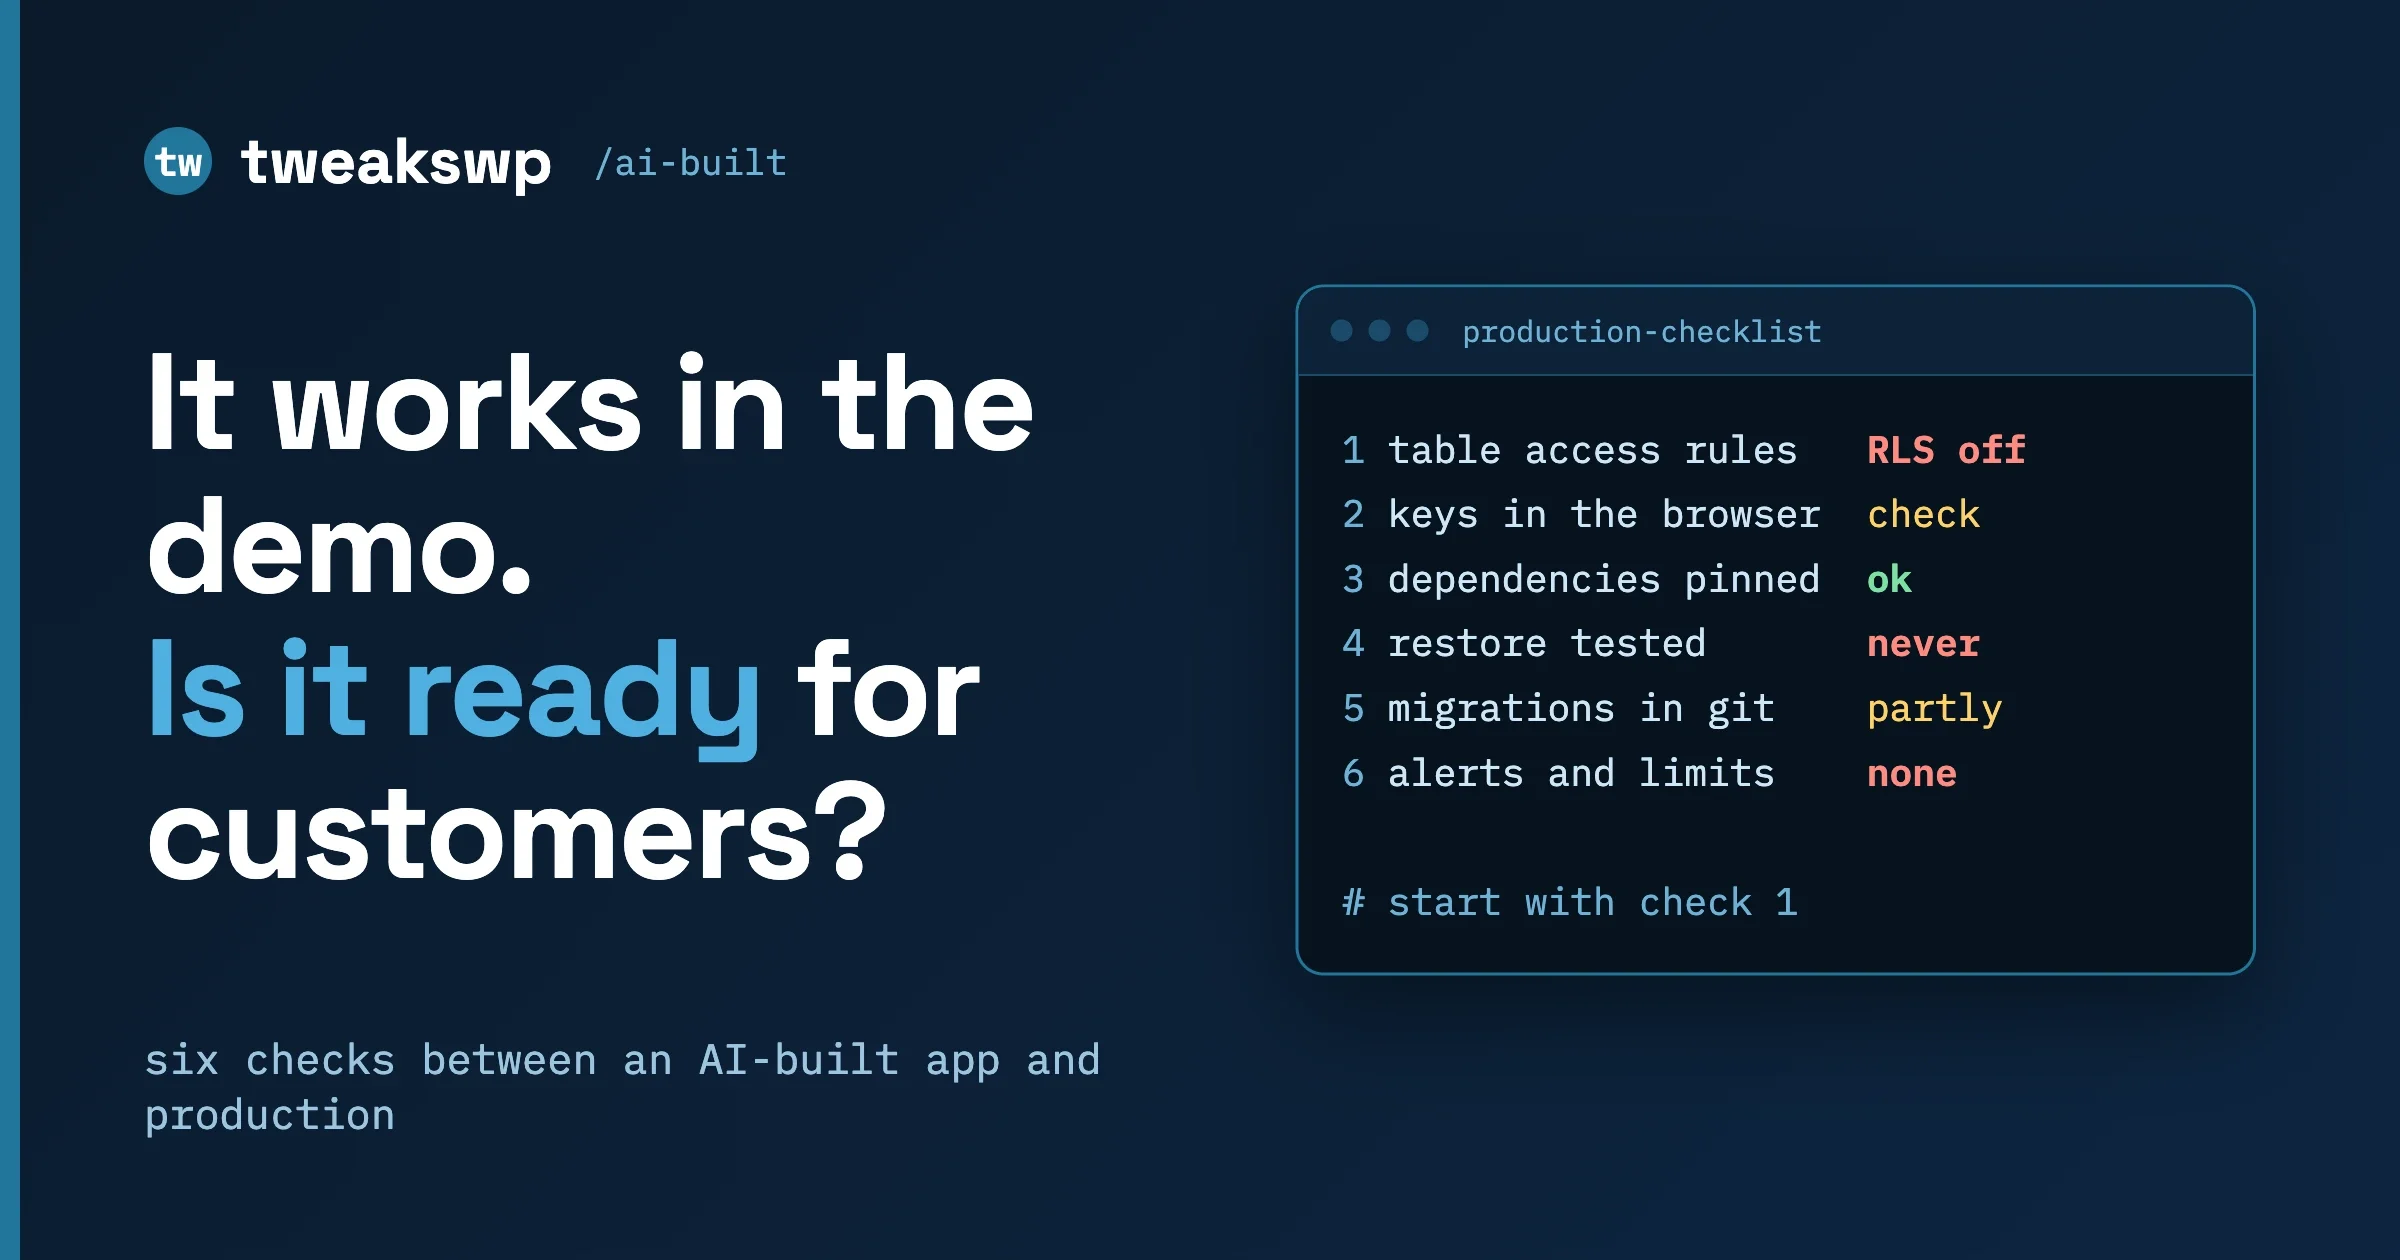
Six checks to run before customers use an app an AI builder made: access rules, keys, dependencies, a tested restore, migrations, and monitoring.
Security15 min read
Test a PHP upgrade on staging: debug log, money paths, forced cron and imports, reading the log, and a PHPCompatibilityWP scan.
Debugging & Profiling15 min read
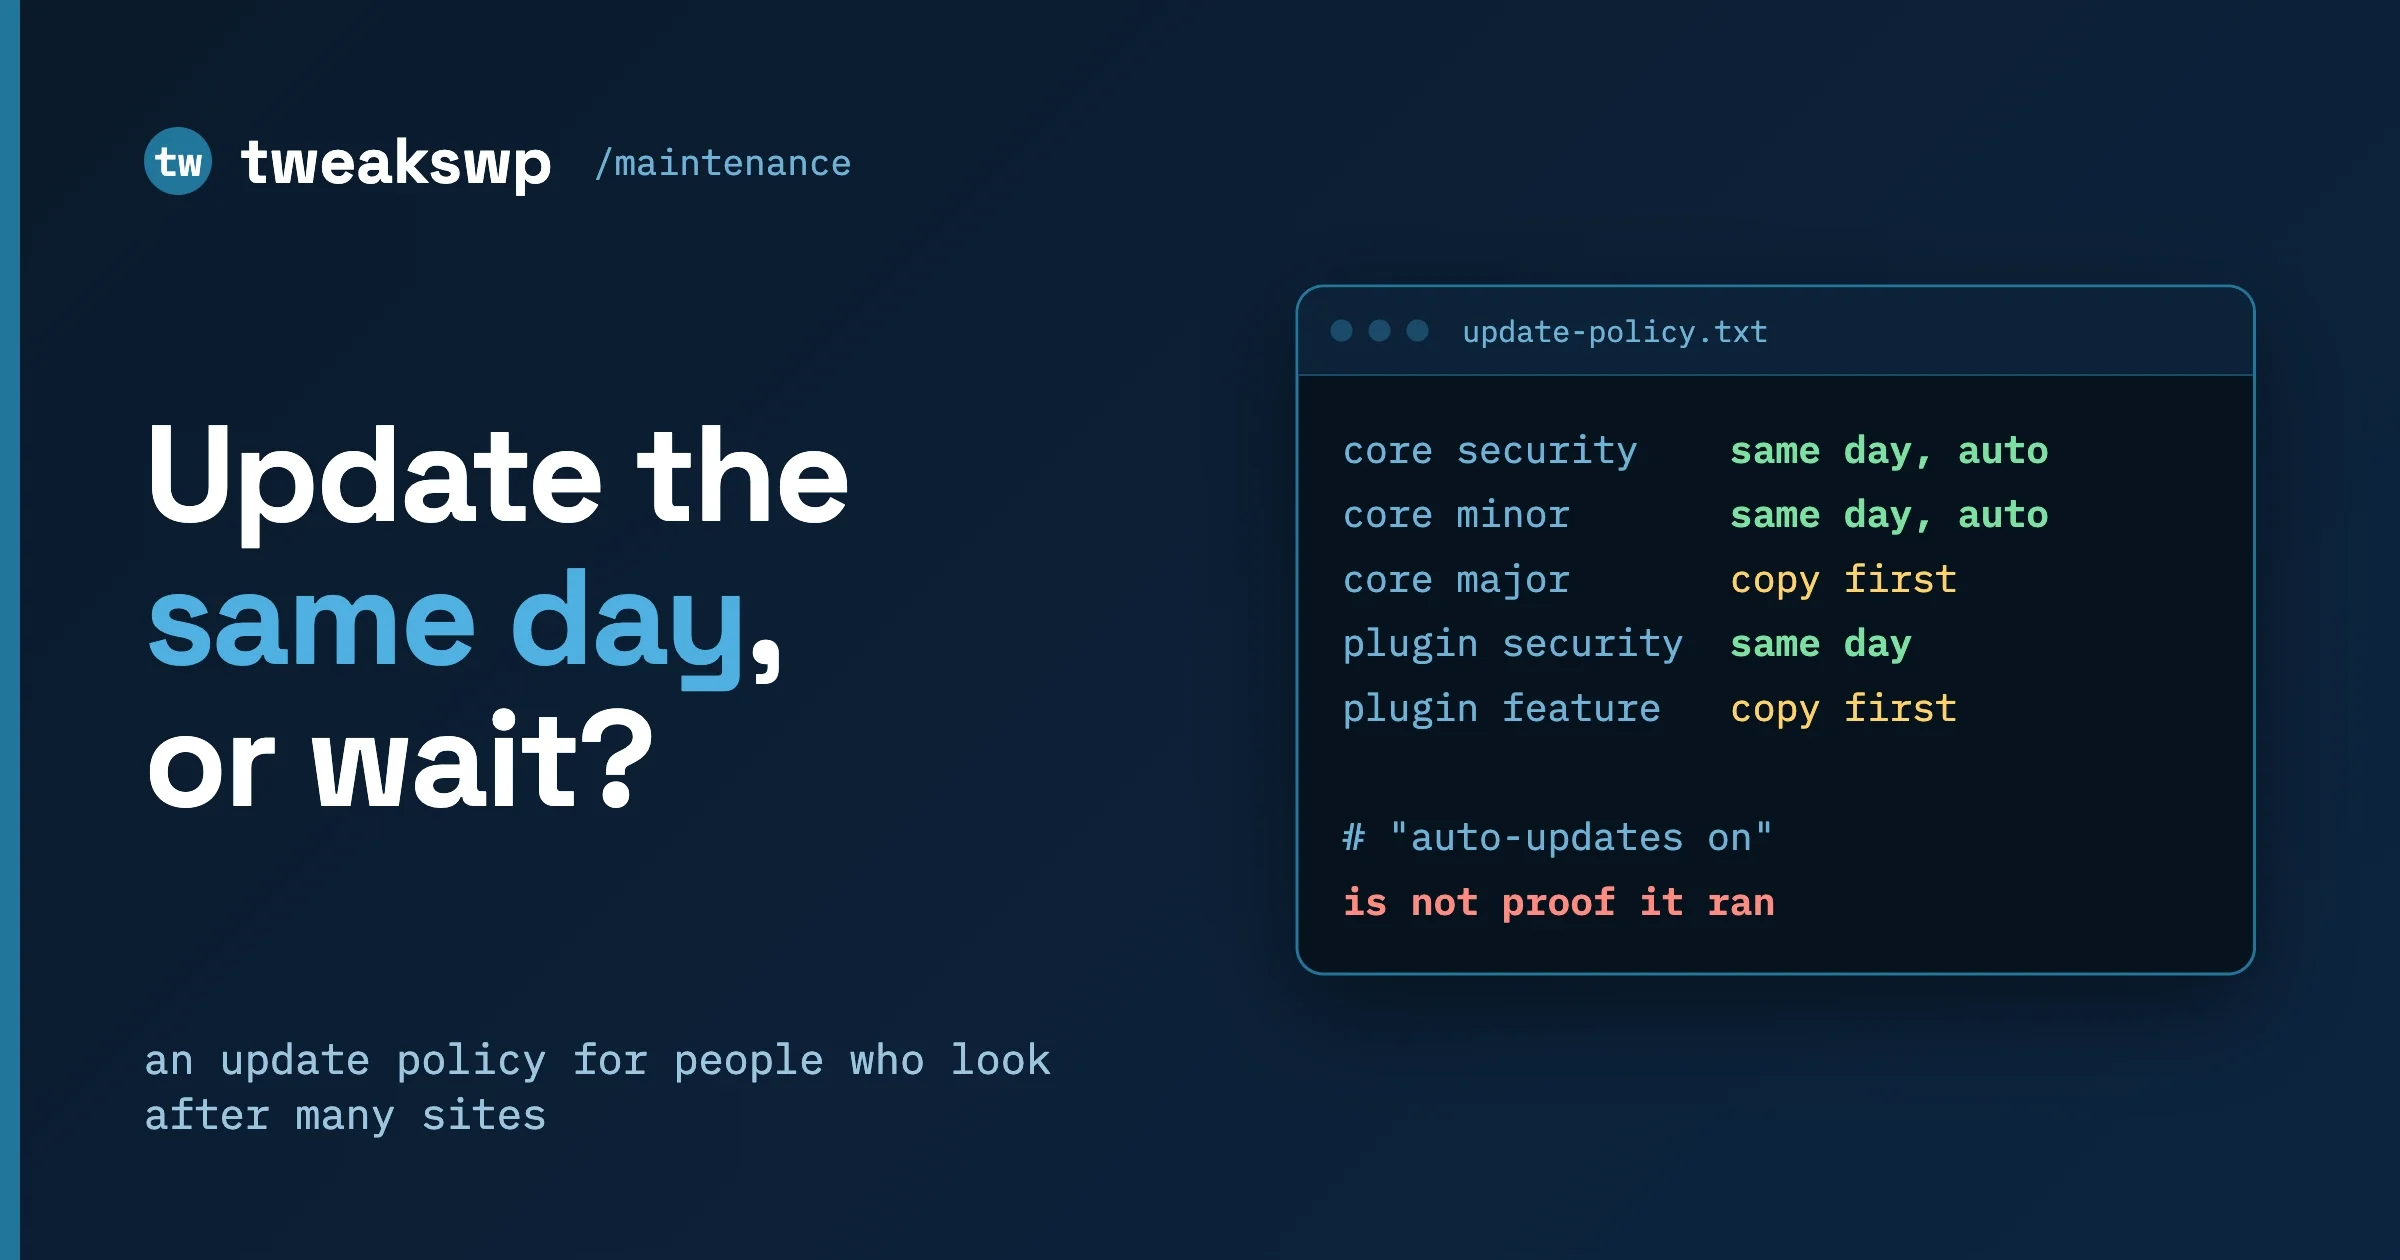
Security releases go out the same day, automatically, with proof. Feature releases get a copy first. A decision table, a three-step check and a rollback plan.
Security15 min read
Some attacks create an admin account the Users screen cannot show. Run this 15-minute WP-CLI and SQL audit, then clean up and prevent a repeat.
Security16 min read
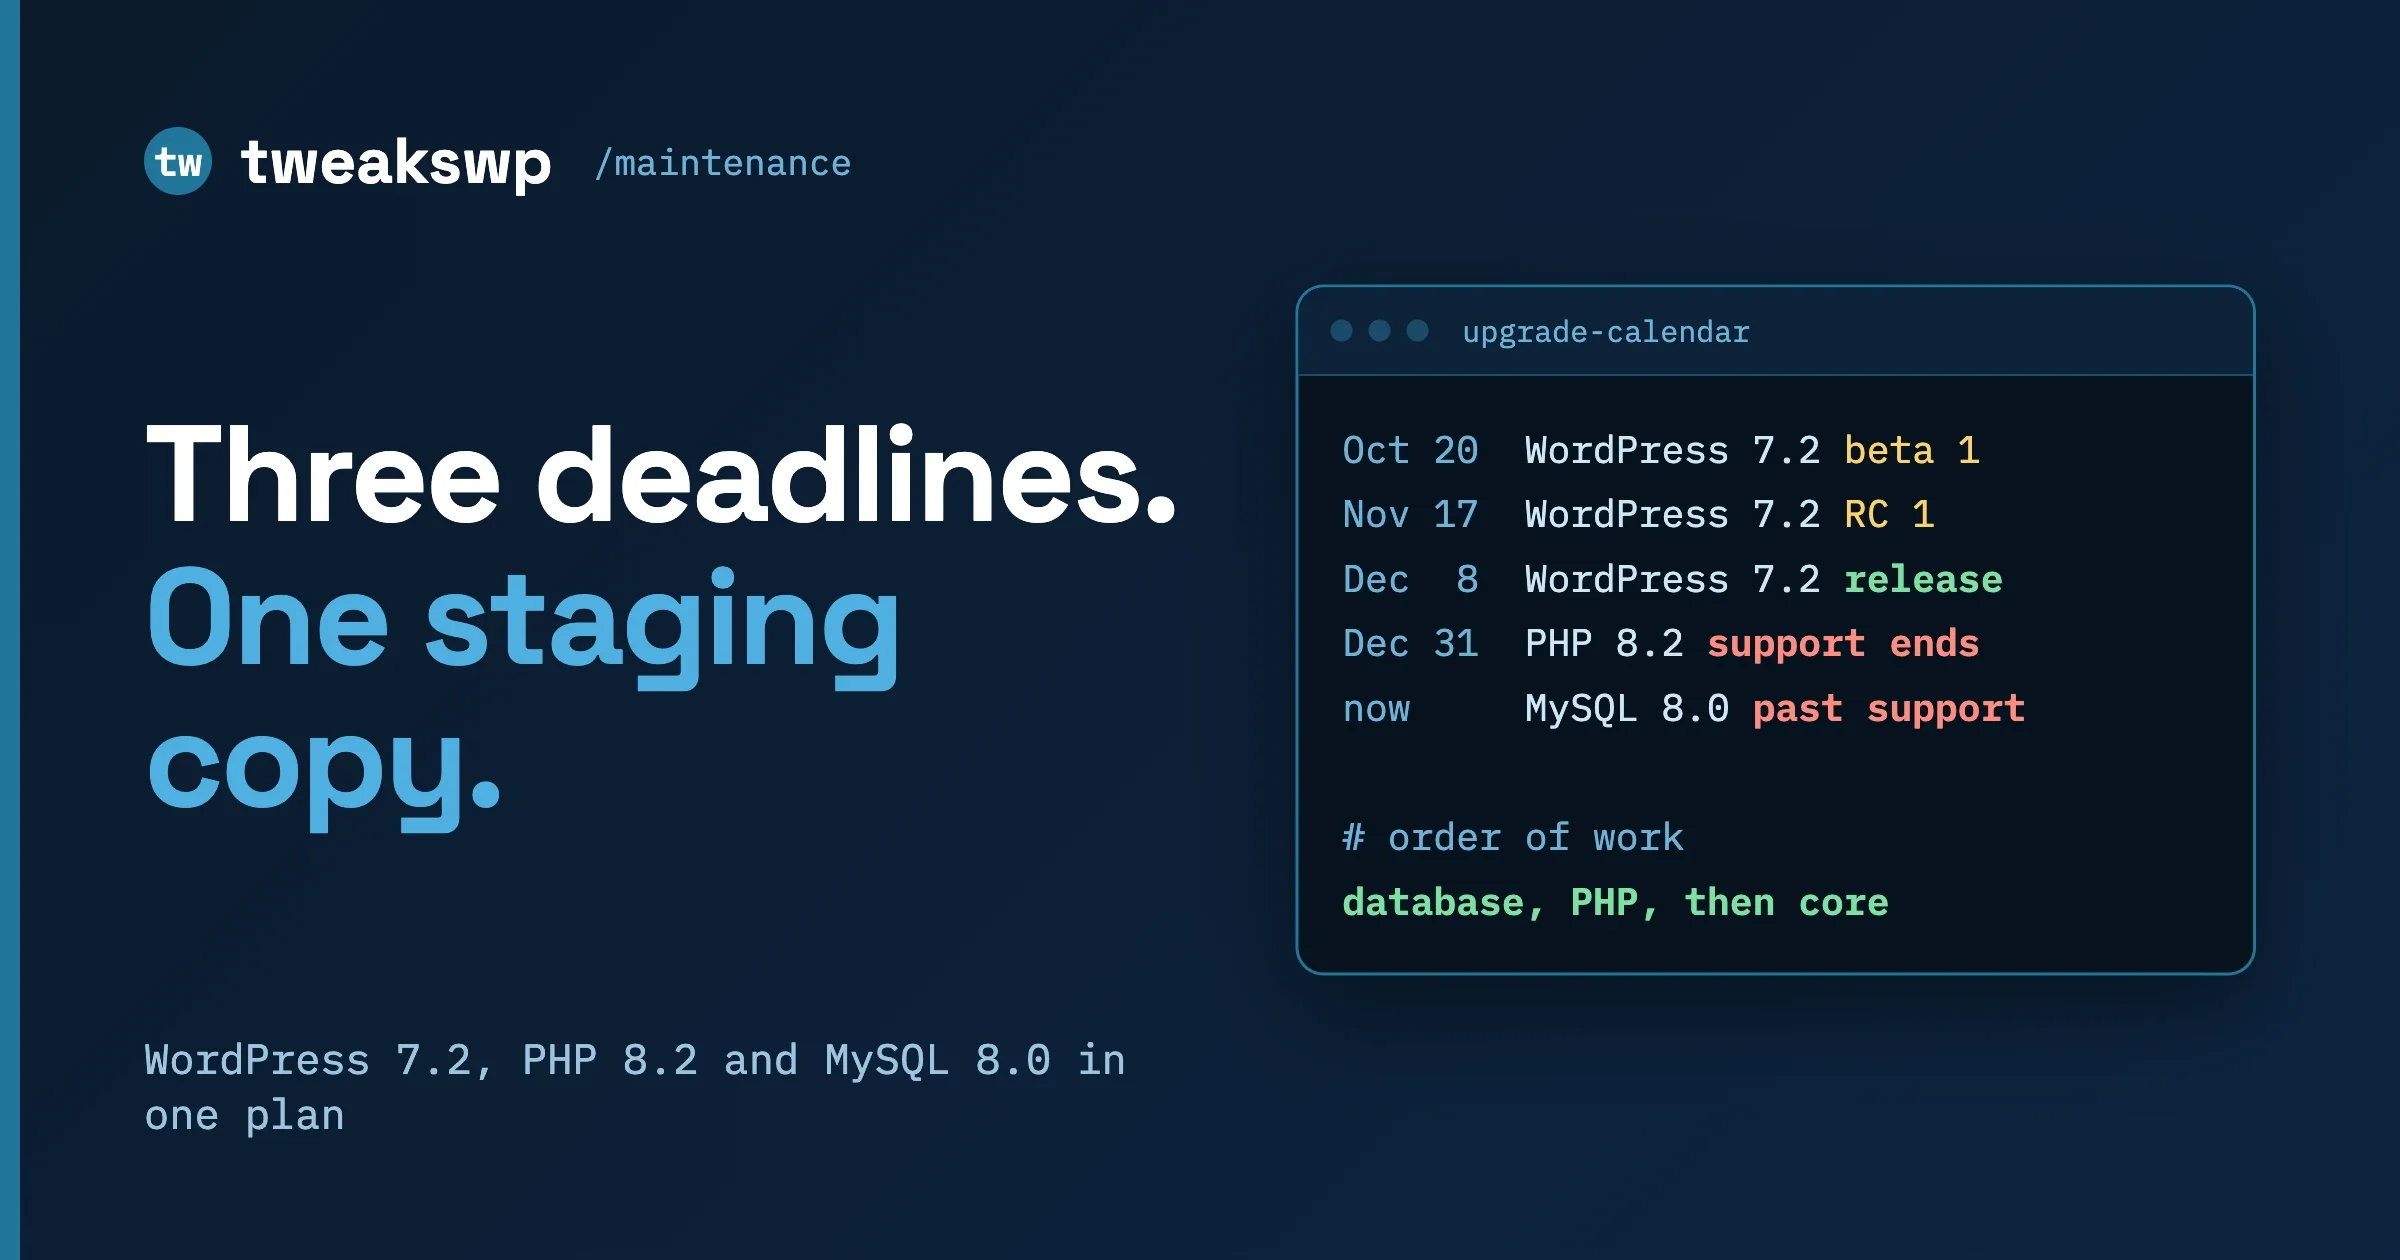
A week-by-week staging plan for WordPress 7.2, the PHP 8.2 deadline and MySQL 8.0, from 12 October to early January, with commands and rollbacks.
Security14 min read
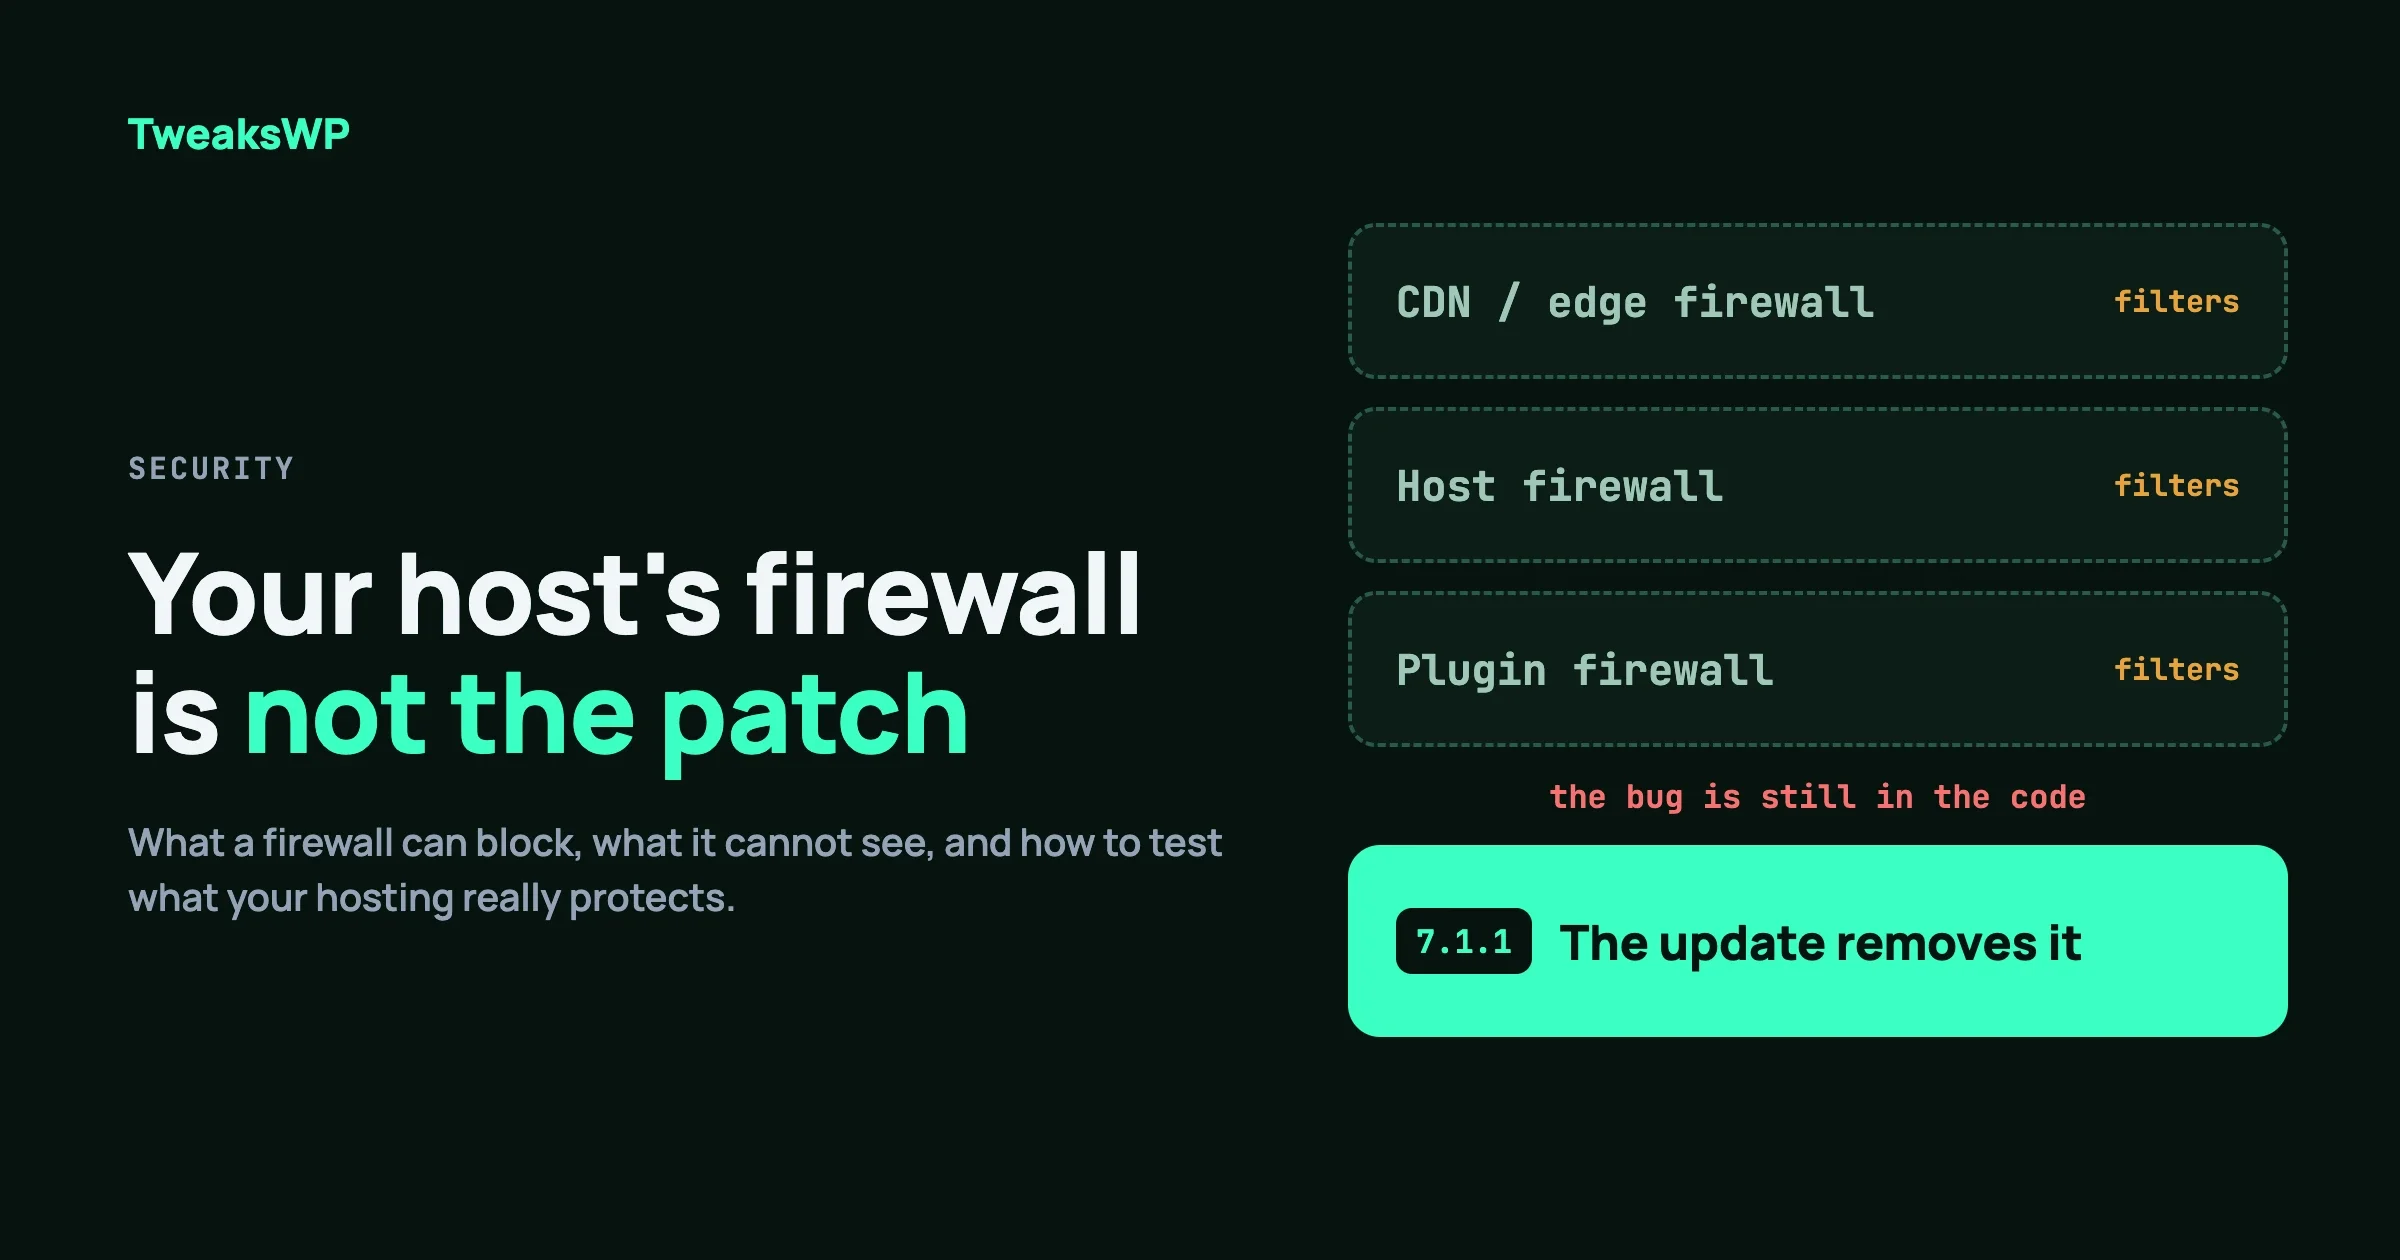
A firewall filters requests that look like a known attack; an update removes the bug. Real WordPress releases where the bug needed a login, which layer filters what, how to test your own protection on staging, and a one-page response plan.
Security12 min read
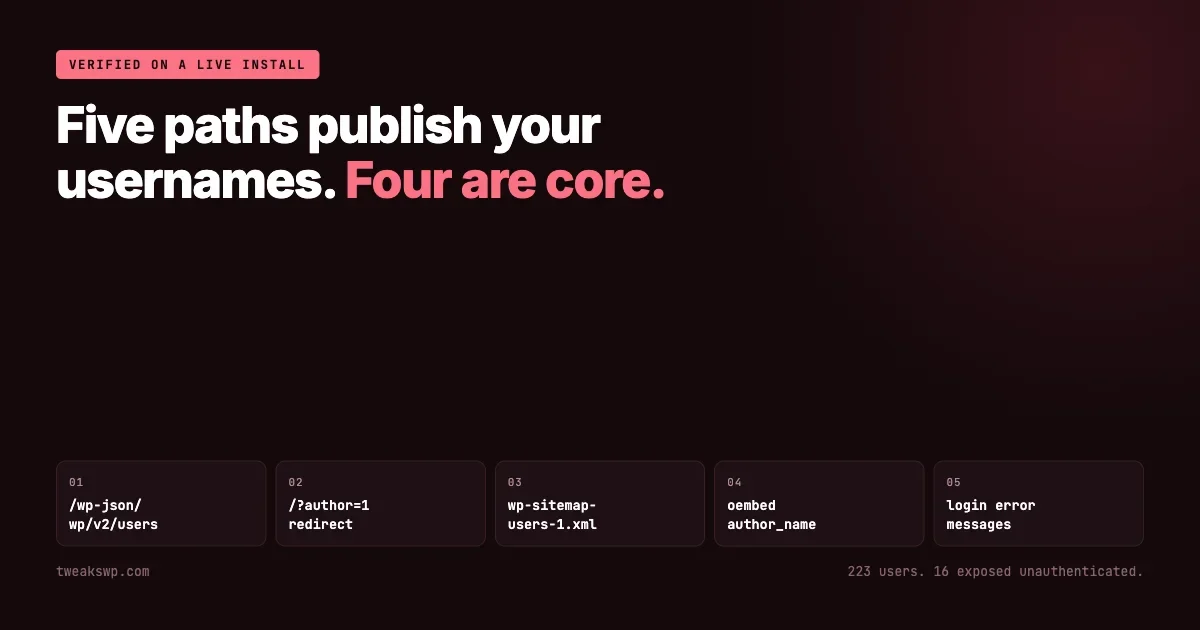
WordPress publishes usernames through five separate paths, most of them core behaviour. Each one tested against a live install, with the fix, the fleet audit, and what to do first instead.
Performance11 min read
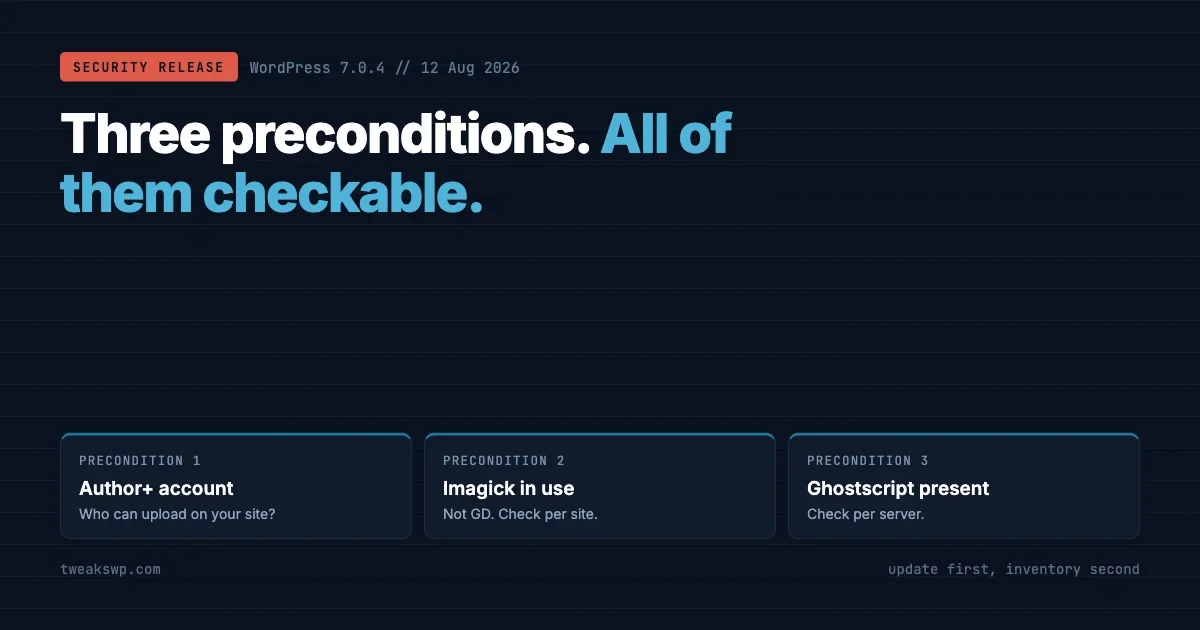
An authenticated Author+ RCE via file upload on sites using Imagick and Ghostscript. Three checkable preconditions, the WP-CLI to answer each across a fleet, and what the CVE record does not yet say.
How To10 min read
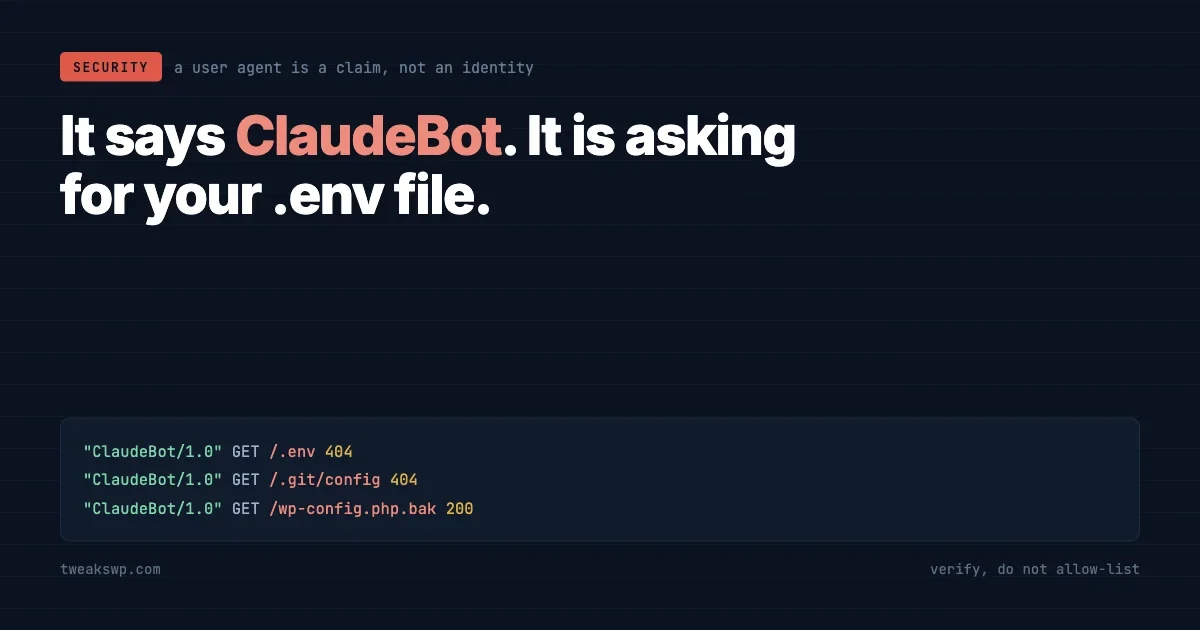
A reported campaign impersonates AI crawlers to scan for credential and config files left by AI coding tools. Why user-agent rules are theatre, how to verify a crawler properly, and the commands to check your own fleet.
AI11 min read
Discovery got faster on both sides. Distribution of the fix did not. What AI actually changed about finding plugin bugs, what it did not, and the WP-CLI commands to measure your own exposure window.
AI11 min read
The all-in-one WordPress community stack
Also ours: wbcomdesigns.comvapvarun.combrndle.com