Best Open Source Community Platforms in 2026: Complete Comparison
Compare the best open source and self-hosted community platforms in 2026: BuddyNext, BuddyPress, Discourse, HumHub, Flarum, NodeBB, and OSSN.
WordPress16 min read
Compare the best open source and self-hosted community platforms in 2026: BuddyNext, BuddyPress, Discourse, HumHub, Flarum, NodeBB, and OSSN.
WordPress16 min read
Compare the 10 best WordPress community plugins in 2026. BuddyNext leads as the complete platform, feed, memberships, courses, forums, and gamification in one system you own.
Membership Websites16 min read
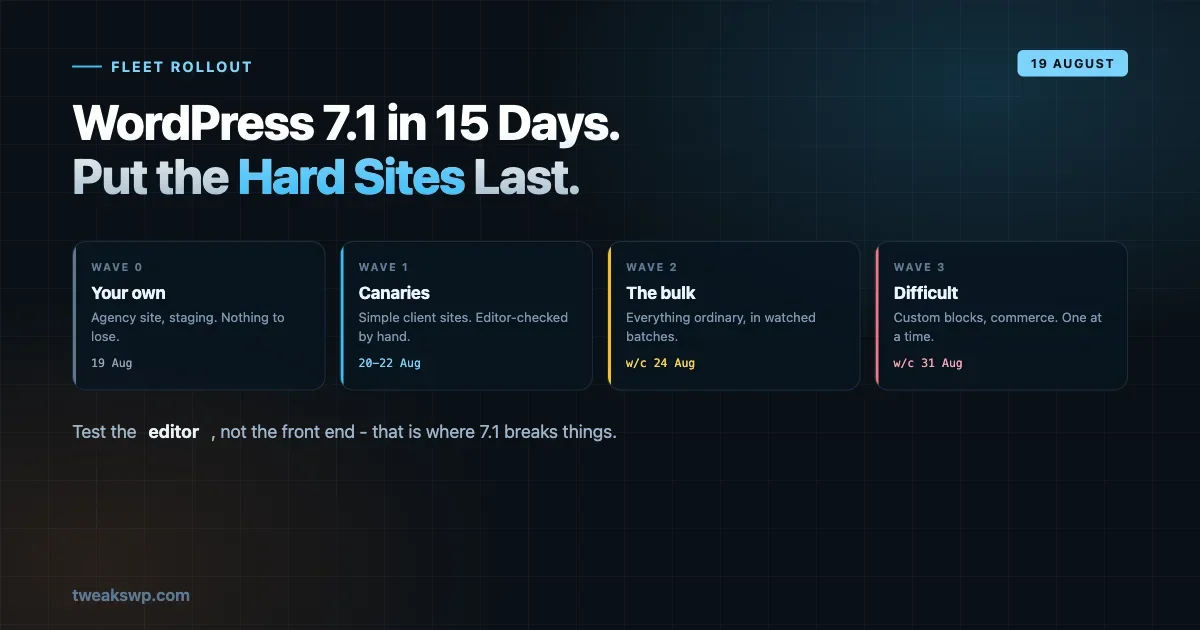
WordPress 7.1 ships 19 August. A staged four-wave rollout for agencies: the inventory commands, which sites go last, what to verify where, the rollback decision, and why front-end smoke tests will miss everything.
How To7 min read
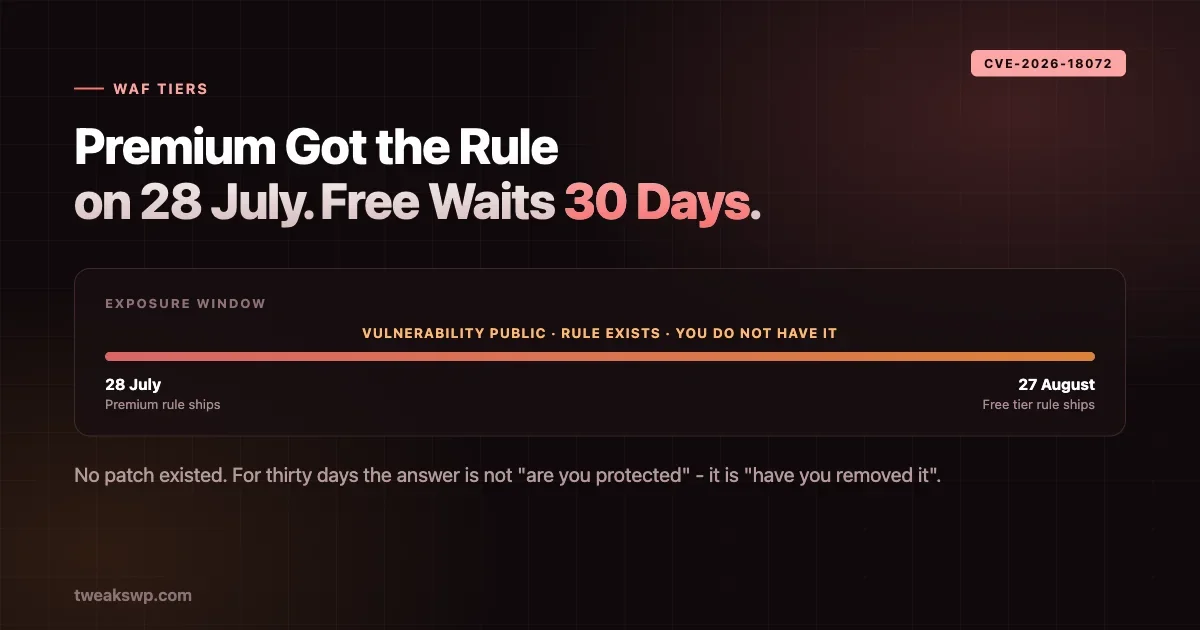
Wordfence shipped the ARVE backdoor rule to premium on 28 July. Free tier gets it 27 August. How to measure your own exposure window, verify the WAF is actually loaded, and four ways to close the gap.
Security12 min read
Media library infinite scroll is on by default in WordPress 7.1. The new precedence order, why setting the filter overrides every user's opt-out, WP-CLI commands to measure your own library, and the three plugin patterns this breaks.
Performance12 min read
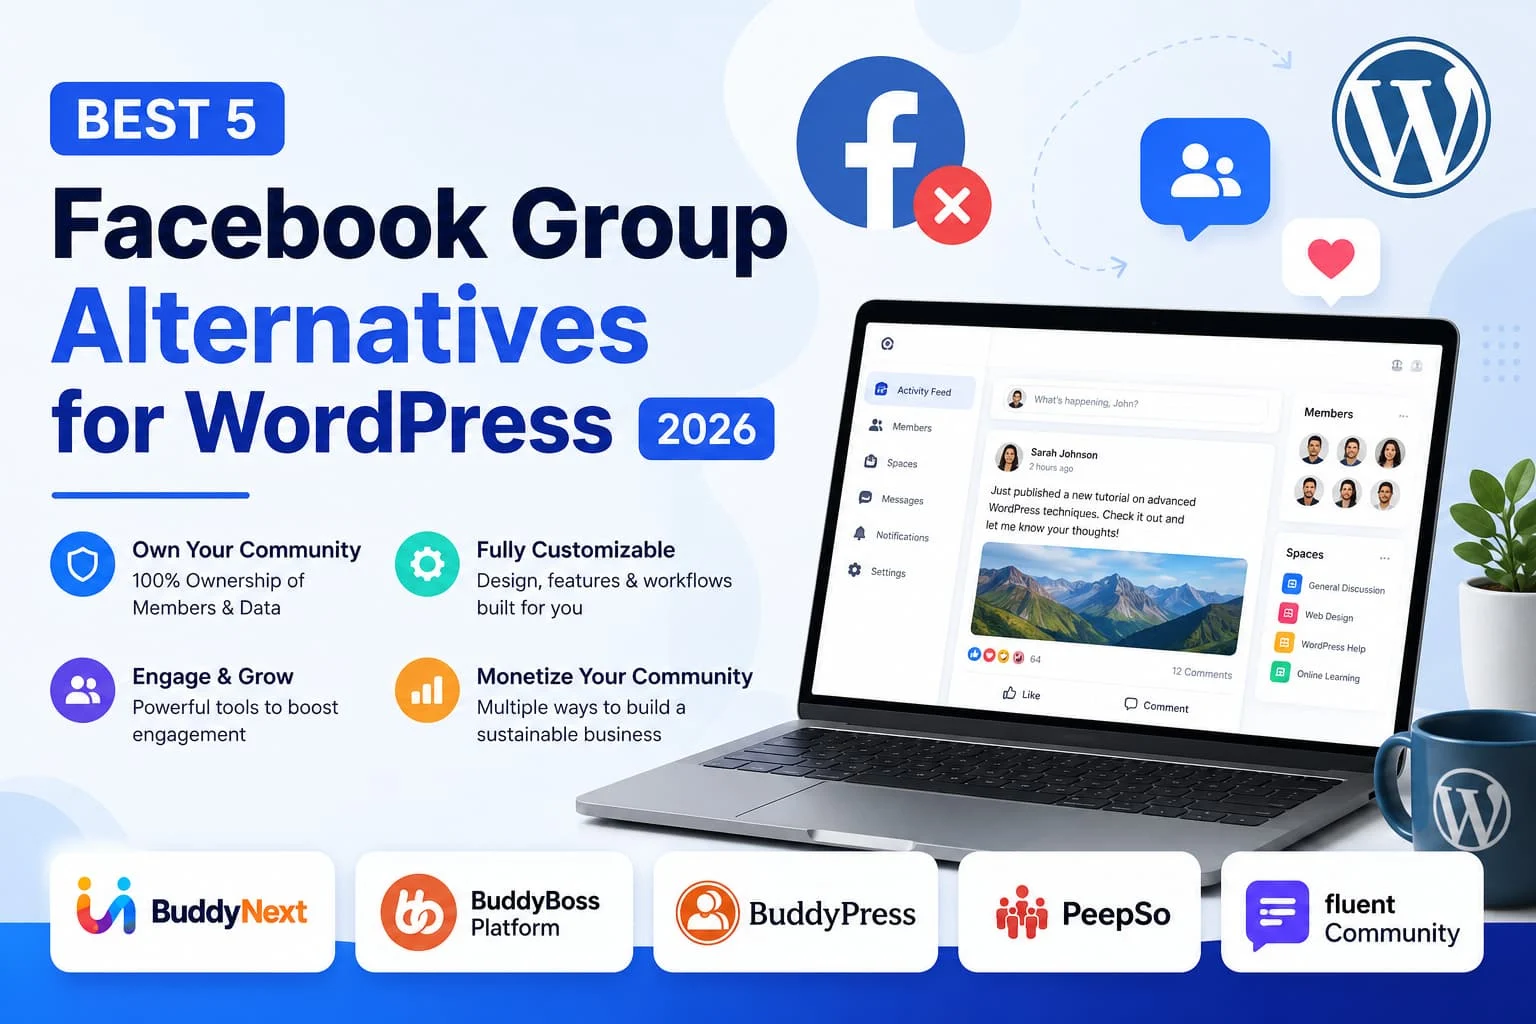
Membership Websites4 min read
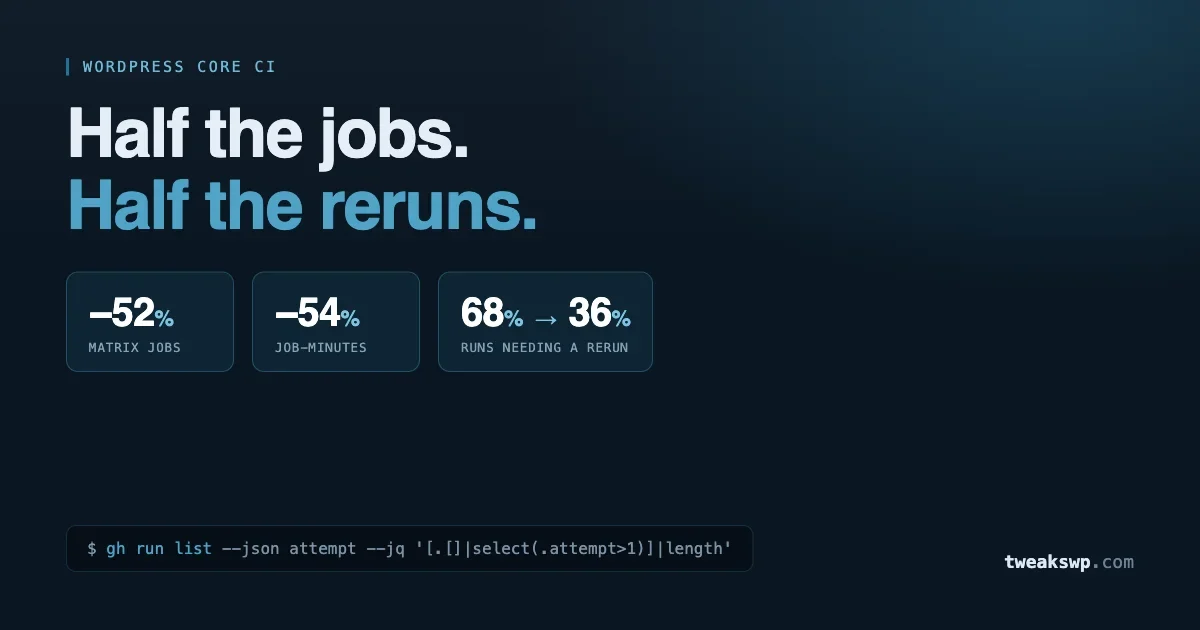
Core cut its PHPUnit matrix by 52 percent and halved its rerun rate. How to apply the same reasoning to a plugin test suite.
Code Snippets10 min read
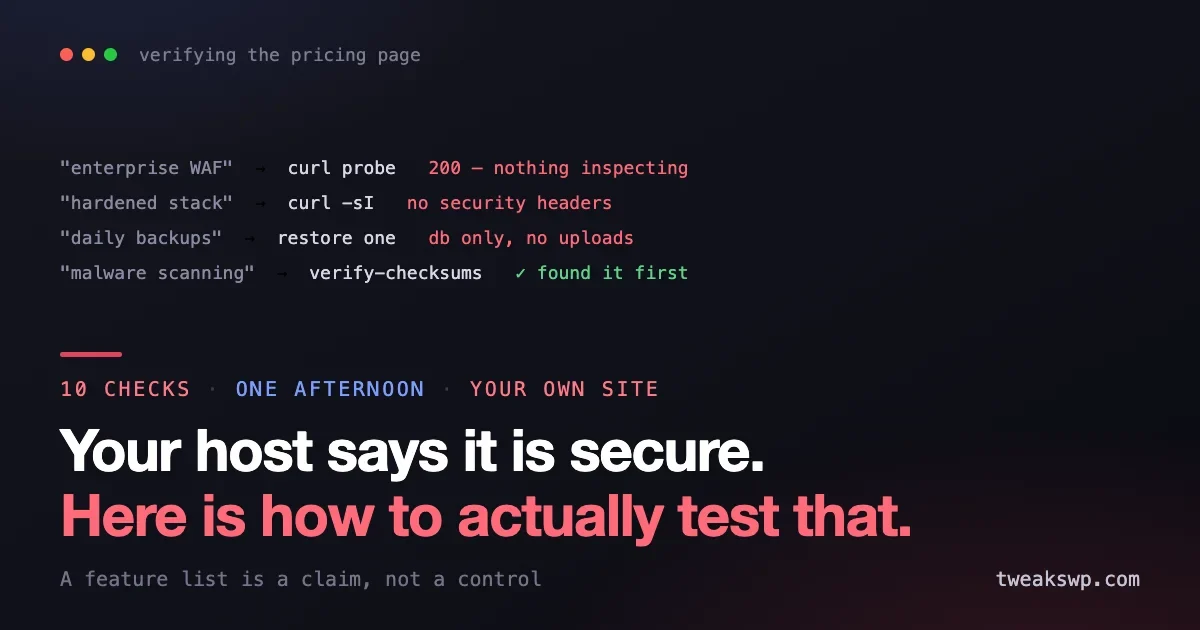
WAF, malware scanning, isolation, daily backups. Every host lists them and almost none of it is verifiable from the marketing page. Ten checks you can run yourself to find out which claims are real, and the questions worth asking before you buy.
Security9 min read
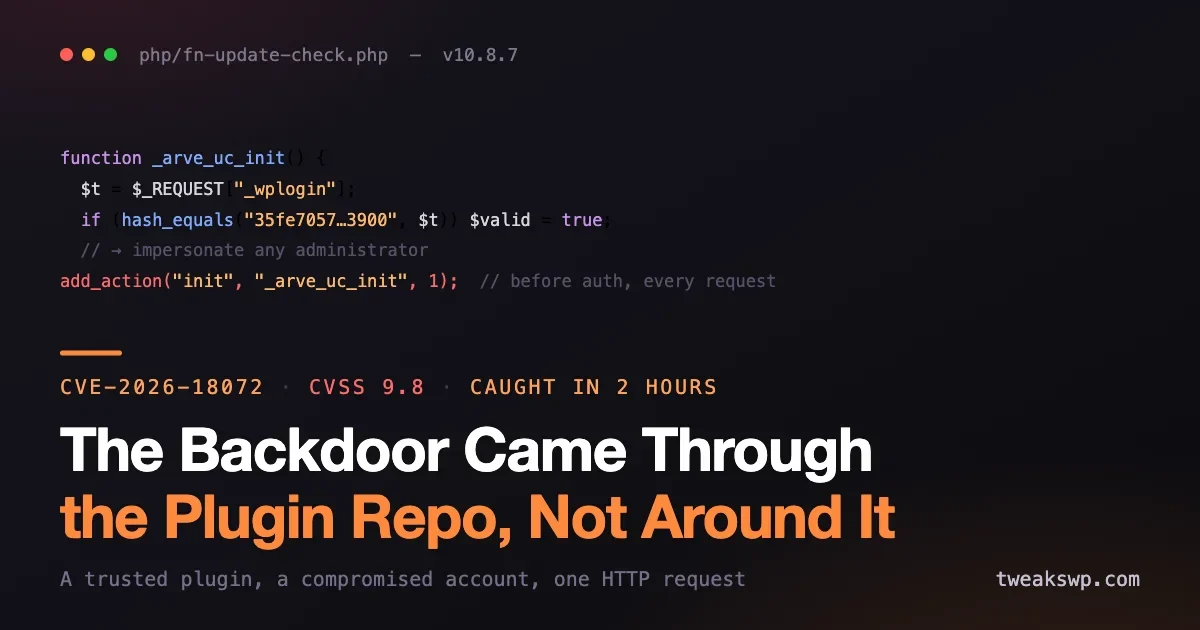
A hardcoded backdoor reached version 10.8.7 of a 20,000-install WordPress plugin via a compromised developer account. It was caught in under two hours and never distributed. What it did, why the detection matters more than the damage, and what it says about trusting the repo.
Security9 min read
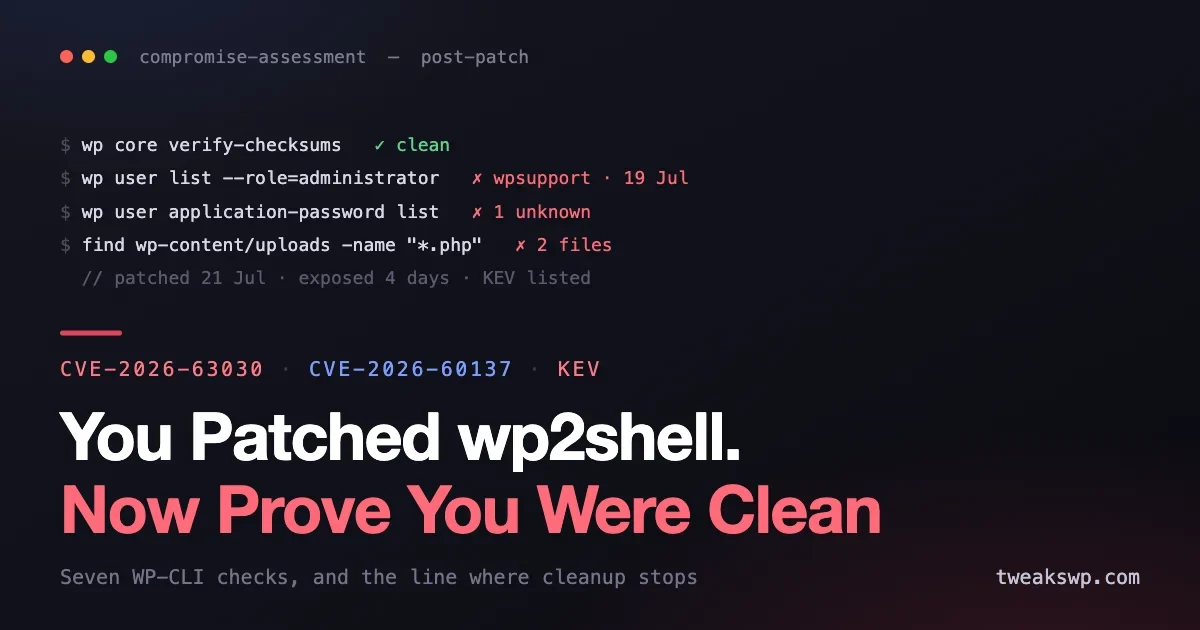
Both wp2shell CVEs went into CISA's KEV catalog on 21 July and public exploits are circulating. Patching closed the door; it did not tell you whether anyone was already inside. A WP-CLI compromise-assessment runbook, and the line where cleanup stops and rebuild begins.
Security10 min read
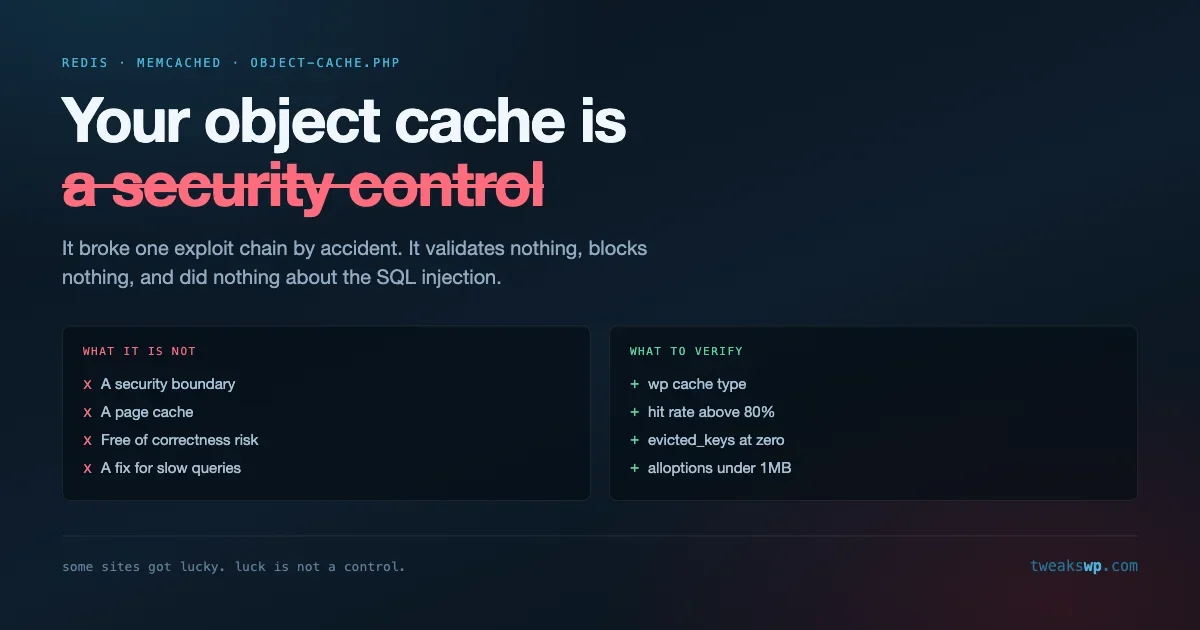
Redis interfered with a recent WordPress exploit chain by accident, not by design. What a persistent object cache actually does, the four things it does not, and how to verify yours is correct rather than merely present.
Performance11 min read
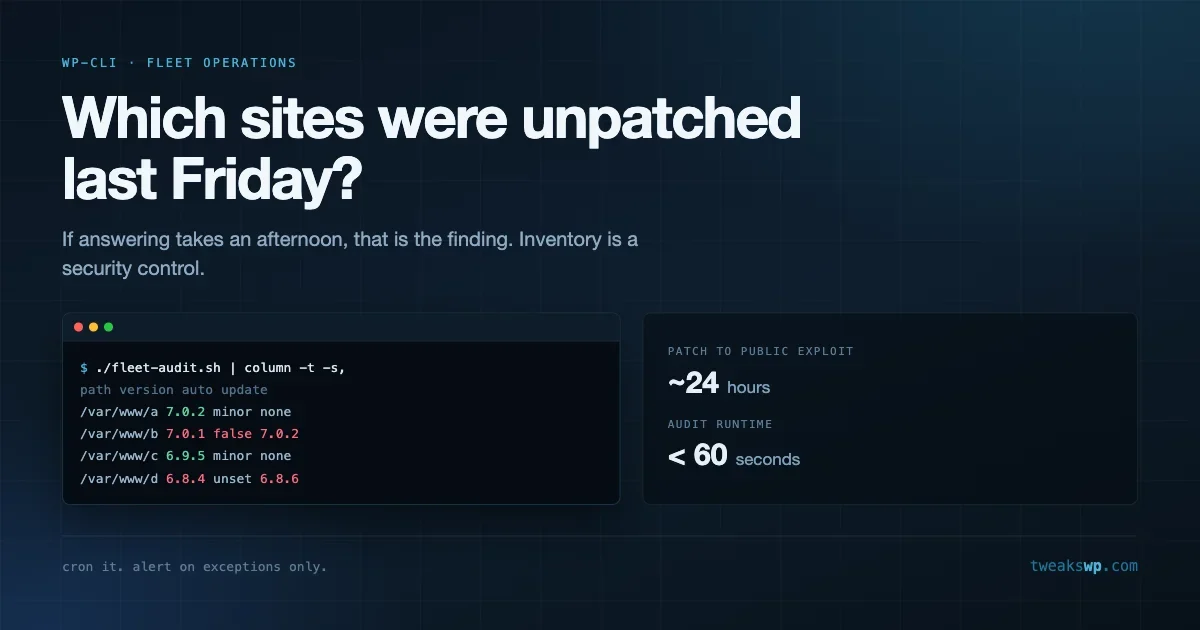
Which of your sites were unpatched last Friday? A defensible auto-update policy, a WP-CLI fleet inventory you can query, verification that runs itself, and an emergency patch path for the next zero-day.
How To11 min read
The all-in-one WordPress community stack
Also ours: wbcomdesigns.comvapvarun.combrndle.com