PHP2Shell: Check Your WordPress PHP Version Now, and What to Do If You Cannot Patch
How to check whether your WordPress site's PHP is patched for CVE-2026-109618 and CVE-2026-109619, which releases fix it, and what to do on PHP 8.1.

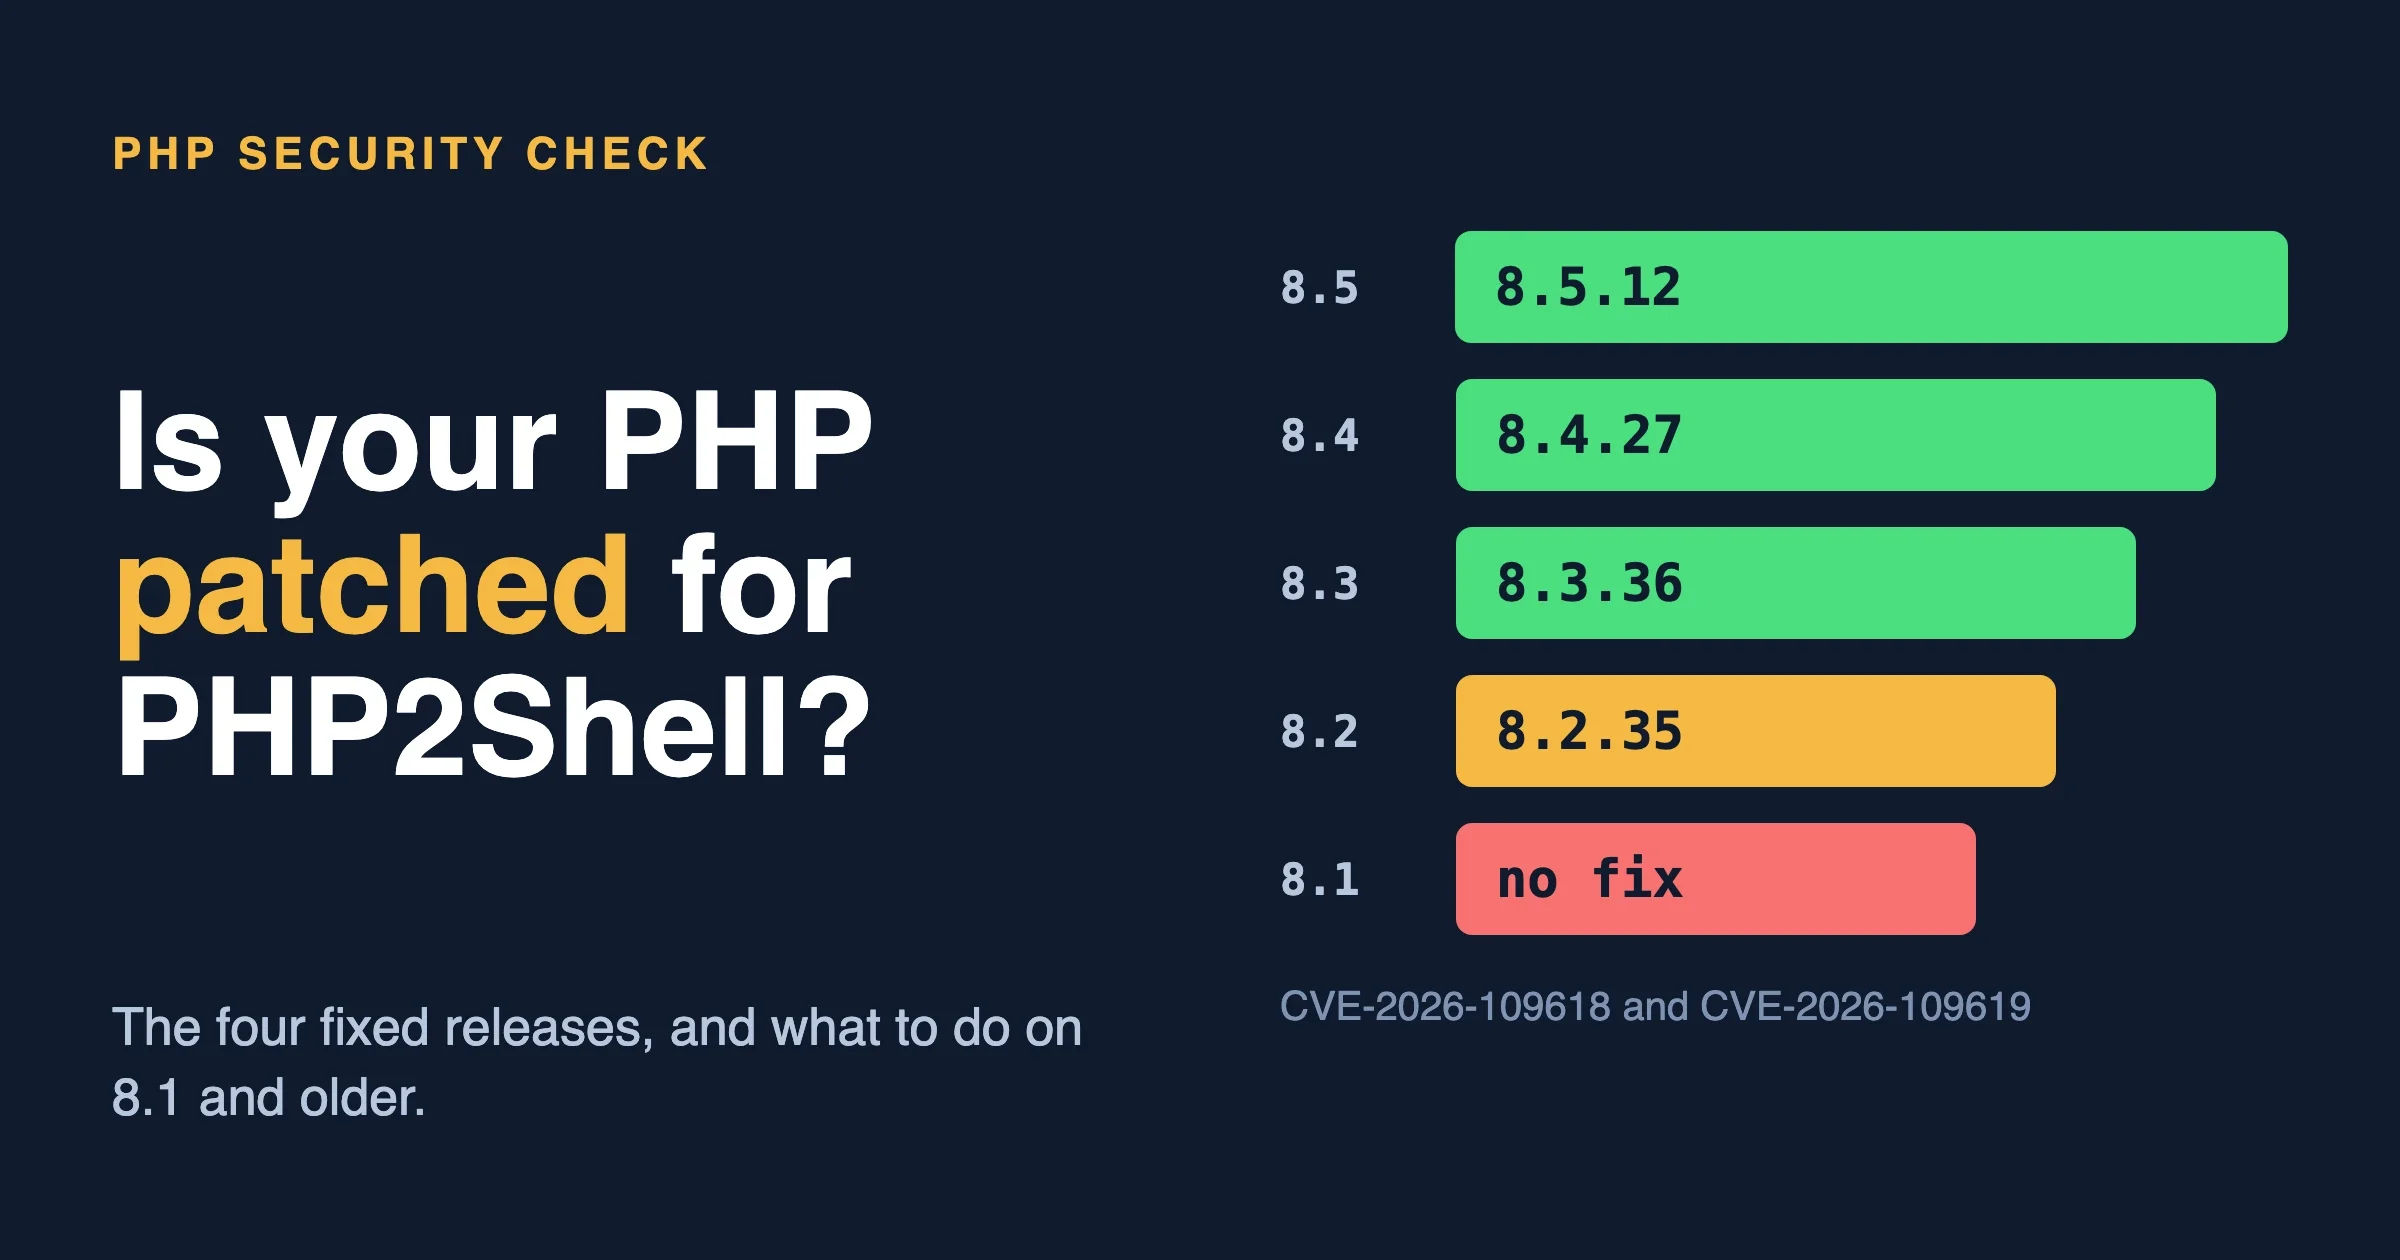
If your WordPress site runs PHP 8.2, 8.3, 8.4 or 8.5, it is safe from the PHP2Shell flaws only when the PHP build serving your pages is 8.2.35, 8.3.36, 8.4.27 or 8.5.12 or newer, or a vendor build whose changelog names CVE-2026-109618 and CVE-2026-109619. Nothing in WordPress or any plugin can fix this, because the bug sits in PHP itself. If you run PHP 8.1 or older, the PHP project shipped no fixed release for you, so you need a vendor backport or a move to a supported branch. We re-checked every identifier, version and date below against primary sources on 15 November 2026.
What is PHP2Shell, and is the name official?
PHP2Shell is a nickname, not an identifier. The official identifiers are two CVE records published on 21 October 2026. Wiz uses the name in its research write-up, and CISA’s alert says the flaws are “dubbed” php2shell. None of the pages we read says who coined it, so we treat it as a widely used label and use the CVE numbers whenever precision matters. Our earlier version of this guide said Wiz reported the bugs and named them. The Wiz timeline does say it reported them to the PHP security team on 24 August, but we found no source that credits Wiz with the name, so we dropped that claim.
Item | CVE-2026-109618 | CVE-2026-109619 |
|---|---|---|
php.net title | RCE via OOM corruption | RCE via stale global state |
Published | 21 Oct 2026 | 21 Oct 2026 |
Severity | 9.2 Critical (CVSS v4.0, set by the PHP CNA) | 9.2 Critical (CVSS v4.0, set by the PHP CNA) |
php-src advisory | GHSA-w8hw-w9fx-j79w | GHSA-6wmf-4rv5-p3rp |
Fixed in | 8.2.35, 8.3.36, 8.4.27 or 8.5.12 | Same four releases, all out 21 Oct 2026 |
Checked on 15 November 2026 against the php.net news archive, the CVE record data served by the CVE Program, and the NVD record. Both CVEs are in the CISA Known Exploited Vulnerabilities catalog, added 26 October 2026 with a due date of 29 October for US federal agencies.
Which PHP versions are affected?
The CVE records list the affected ranges as everything below 8.2.35, 8.3.36, 8.4.27 and 8.5.12 on those four branches. The NVD configuration for CVE-2026-109619 goes further back and starts at PHP 5.4.0, which matches the Wiz statement that every release of the last decade is affected by at least one of the bugs. php.net’s advisory gives no range of its own. It says PHP 8.1 and older no longer receive updates from the PHP project, and it links source-only backports for 7.4, 8.0 and 8.1. We read the records this way: the four supported branches have an upstream fix, and older branches are exposed unless a vendor patched them.
What did php.net say to do?
Update. The release notes for 8.5.12, 8.4.27 and 8.3.36 say there are no complete mitigations and that updating is the only safe choice. The 8.2.35 notes add that PHP 8.2 reaches end of life on 31 December 2026. CISA’s alert and the NCSC-NL tracker both say every PHP installation serving web requests is in scope (Apache mod_php, PHP-FPM, php-cgi, FrankenPHP and LiteSpeed), and the tracker says PHP rates the risk highest for mod_php, where a request can trigger the attack before any application code runs. That is why a security plugin is not a defence: it is PHP code that loads after the interpreter has already taken the request.
PHP branch | Patched release | Upstream security support ends |
|---|---|---|
8.5 | 8.5.12 | 31 Dec 2029 |
8.4 | 8.4.27 | 31 Dec 2028 |
8.3 | 8.3.36 | 31 Dec 2027 |
8.2 | 8.2.35 | 31 Dec 2026 |
8.1 and older | No upstream release | Already ended |
Support dates are from the php.net supported versions page, read 15 November 2026.
How do I check my PHP version in WordPress?
Open Tools, then Site Health, then the Info tab, and expand the Server section. It shows the PHP version and the PHP SAPI, which is the way PHP attaches to the web server (FPM, Apache module, CGI or LiteSpeed). WooCommerce’s guidance points to the same screen. This is the number your visitors reach, so it is the one that counts. Write down the SAPI too, because it tells you which service to restart after an update.
The Site Health Status tab can warn that PHP is out of date by WordPress’s own standard. It cannot tell you whether your build has the 21 October patch, so read the exact version string, not the colour of the badge. Check every other site on the same server too, including staging copies and the old install nobody took down.
Can WP-CLI tell me?
Partly, and with a trap. WP-CLI reports the PHP binary on the shell’s path, which on many servers is not the one the web server uses. A cPanel or Plesk machine with several PHP versions can answer 8.3 on the command line while the site runs 7.4.
wp cli info | grep -i "php binary\|php version"
wp eval 'echo PHP_VERSION . " " . PHP_SAPI . "\n";'
Checked on 15 November 2026 with WP-CLI 2.12.0: wp cli info prints the labels “PHP binary” and “PHP version”. The second command prints the SAPI as cli, which is the proof that it describes the command line, not the website. Treat both as the version of the tool and Site Health as the version of the site.
Is phpinfo() safe to use?
It is the quickest way to read the web value of any setting, and it is a risk if you leave it up. The output lists your configuration, file paths, loaded modules and environment details, which is exactly the reconnaissance an attacker wants before targeting a server. If you use it, put the file somewhere that needs a login or an IP allow-list, load it once, and delete it in the same sitting. Never name it phpinfo.php in the web root and walk away. For the version alone, Site Health gives you the answer without creating a file at all.
If you want a pass or fail against the fixed releases, this script compares the running version to the floor for its branch. Run it with the binary your FPM pool uses, and delete it afterwards if you place it under a web path.
<?php
// Patched floor per supported branch (php.net advisory, 21 Oct 2026).
$floor = array( '8.2' => '8.2.35', '8.3' => '8.3.36', '8.4' => '8.4.27', '8.5' => '8.5.12' );
$branch = PHP_MAJOR_VERSION . '.' . PHP_MINOR_VERSION;
if ( isset( $floor[ $branch ] ) ) {
	$ok = version_compare( PHP_VERSION, $floor[ $branch ], '>=' );
	echo PHP_VERSION . ' (' . PHP_SAPI . '): ' . ( $ok ? 'at or above the fixed release' : 'below the fixed release, need ' . $floor[ $branch ] . ' or a vendor build that lists the CVEs' ) . "\n";
} else {
	echo PHP_VERSION . ' (' . PHP_SAPI . '): no upstream fix on this branch, ask your vendor about a backport' . "\n";
}
Syntax-checked with php -l and run on 15 November 2026 on a laptop with Homebrew PHP 8.5.5, where it printed that the build is below the fixed release and needs 8.5.12. That is the correct answer for that build.
My version is below the floor. Am I unpatched?
Not necessarily. Distribution and hosting packages often carry a fix without changing the upstream version string. Patchstack’s alert notes that Ubuntu 22.04’s PHP 8.1 package is patched as 8.1.2-1ubuntu2.28 while still calling itself 8.1. The WPVanguard hosting status page, last checked 22 October, says CloudLinux EasyApache builds dated 21 October still reported 8.3.35 and 8.4.26 while their changelogs listed both CVEs. So a low number is a reason to read the package changelog, and a number at or above the floor is the simple good case.
# Debian and Ubuntu
apt changelog php8.3-common | grep -i "CVE-2026-10961" | head

# RPM based systems (AlmaLinux, CloudLinux, RHEL): adjust the package name
rpm -q --changelog ea-php83-php-common | grep -i "CVE-2026-10961" | head
If the changelog names both CVEs, your vendor shipped the fix. If it does not and the version has not moved, assume it has not been fixed. We ran these on no server for this refresh, since package names differ by distribution and panel, so adjust them for yours. On shared hosting where you cannot run any of this, your host’s support is the route.
Who is responsible for patching: me or my host?
It depends on who controls the PHP package. The table is the split we use when we triage a client site.
Your hosting | Who updates PHP | What you still do |
|---|---|---|
Shared hosting | The host | Ask which exact build runs on your plan and when it went live. Check Site Health yourself. |
Managed WordPress hosting | The host | Same question. Automattic platforms (WordPress.com, WordPress VIP, Pressable, WP Cloud) were listed as already protected by the WooCommerce developer blog. |
VPS or dedicated server | You, or whoever manages it | Update the package, restart the workers, verify from the web. |
Docker or containers | You | Pull a patched image, rebuild yours, redeploy, check inside the running container. |
PHP bundled in a panel or appliance | The vendor | Find the vendor notice. The NCSC-NL tracker lists products by status. |
When you write to a host, ask a direct question: which exact PHP build serves my site, and was the 21 October security release applied to the pool that serves it? Keep the answer. “We monitor all security issues” is not an answer. The same logic is in our guide to testing a host’s security claims. WPVanguard keeps a host-by-host status page, last checked 22 October when it showed Cloudways, Kinsta and Hostinger shared servers as patched and several others still rolling out. Hosts change by the hour, so read the page’s own timestamp and confirm with your host.
What are the upgrade steps?
Step 1: patch inside your branch first
Moving from 8.3.30 to 8.3.36 is a patch release, which carries fixes rather than new language behaviour, so it is the lowest-risk move and the right first step for any site you have not tested on a newer branch. On a VPS with Debian or Ubuntu packages, update the packages and restart the service your SAPI uses. These commands assume PHP 8.3 from a repository that has already published the patched build.
sudo apt update
sudo apt install --only-upgrade php8.3-fpm php8.3-cli php8.3-common
php8.3 -v
sudo systemctl restart php8.3-fpm
# Apache with mod_php instead of FPM:
sudo systemctl restart apache2
The restart is part of the fix. A long-lived worker keeps running the old code in memory until it is restarted. After the restart, confirm the version again in Site Health.
Step 2: set the interim PHP setting while you plan
php.net’s 23 October informational advisory covers a third identifier, CVE-2026-115560, which it calls an unlikely RCE vector. It asks you to set the line below until the next regular bugfix release and says a full advisory will follow with that release. The NCSC-NL repository gives the same advice for sites that do not need the feature.
; php.ini or the FPM pool config, then restart all workers
session.upload_progress.enabled = 0
Checked on 15 November 2026: the php.net archive lists no new 8.x patch release since 21 October, so this advice still stands. NVD has no record for CVE-2026-115560 yet. The advisory says the issue needs an unusual setup, where an application switches session.serialize_handler at runtime. Most WordPress sites never do, and turning the feature off only matters if something you run shows upload progress bars.
Step 3: choose the branch to settle on
The WordPress requirements page recommends PHP 8.3 or greater, with MariaDB 10.11 or MySQL 8.4 or greater. PHP 8.2 stops getting security fixes on 31 December 2026, so patch it now and schedule the branch move. Our end-of-year upgrade calendar has a week-by-week plan, and our post on what a PHP upgrade will break covers the staging test itself: switch the version on a copy, log errors to a file, click through the pages that earn money and read the log for several days.
Step 4: docker, cPanel and the rest
For containers, pull the current image for your tag, rebuild on top of it and check the version from inside the running container, not from the tag in your file. On cPanel with CloudLinux, update the EasyApache PHP packages, restart the handler and read the changelog rather than trusting the version string. Patchstack lists CloudLinux ea-php packages from ea-php52 through ea-php85 as fixed.
docker pull php:8.3-fpm
docker run --rm php:8.3-fpm php -v
# after rebuilding and redeploying your own image:
docker exec your-wp-container php -v
What if my PHP branch has no upstream fix?
This is the hard case: PHP 8.1, 8.0, 7.4 or older, often because an old plugin or a licence blocks the upgrade. php.net says some distributions and LTS vendors provide backported fixes, so ask your vendor or upgrade. Patchstack’s alert, as of 22 October, lists what existed then. Check your own vendor, because the list kept moving.
Platform | What Patchstack reported |
|---|---|
Debian and Ubuntu (Sury repository) | Covers PHP 5.6 through 8.1. Ubuntu 22.04’s php8.1 is patched as 8.1.2-1ubuntu2.28. |
Ubuntu Pro | Covers 14.04 to 20.04. 14.04 and 16.04 need the Legacy add-on. |
AlmaLinux | Patched streams for 8, 9 and 10, including end-of-life streams. |
RHEL and Remi | Partial. Remi covers 7.4, 8.0 and 8.1 on RHEL 8 and 9, but not 7.2 or 7.3. |
cPanel (CloudLinux) | ea-php52 through ea-php85 packages. |
Paid extended support | TuxCare ELS rolling out per branch. Zend LTS builds of 7.2 to 8.1. |
Docker official image | No fix for 8.1 or older. |
PHP also published source-only backport branches named PHP-7.4-CVE-2026-109618-109619, PHP-8.0-CVE-2026-109618-109619 and PHP-8.1-CVE-2026-109618-109619, which Patchstack labels a last resort. Building PHP from source is fair for a team that already compiles PHP and can rebuild every extension. It is not a plan for someone doing it the first time under pressure.
Are the partial settings worth it?
Patchstack calls these interim mitigations partial and not safe, and php.net says none is complete. We have not tested their effect against the exploit.
- Set
session.upload_progress.enabled=0and restart all workers (relates to CVE-2026-109619). - On PHP 8.5 only, set
fatal_error_backtraces=0and restart workers. - Set
memory_limit=-1where applications cannot override it, and setpost_max_sizeto 8M if the site takes no uploads or 32M if it does (relates to CVE-2026-109618). Unlimited memory lets a runaway request exhaust the server, so use it for a short window only.
php -i on the command line reads the CLI configuration, which may differ from the FPM pool. Read the pool file for the web value.
Will a WAF or Cloudflare cover me?
Only as a stopgap. Patchstack reports that Cloudflare deployed initial WAF rules to all customers, including the free plan, and calls them a stopgap that helps only if your origin accepts traffic exclusively from Cloudflare. If an attacker can reach your server’s IP directly, the filter never sees the request. The test is simple: request your origin IP directly and see whether PHP answers. Treat any plugin that claims to patch PHP2Shell as a likely supply-chain risk, since a PHP-level snippet cannot repair interpreter state.
Should the site go offline?
CISA’s alert says organisations that cannot update right away, or that run PHP 8.1 or earlier, should take PHP-based systems offline until they are patched or upgraded. WooCommerce’s post quotes the UK NCSC in the same direction. For a shop holding customer data on a branch with no fix, that is a legitimate choice. Serve the maintenance page from the web server or CDN, not from PHP, and send an HTTP 503 so search engines read it as temporary. Our post on keeping pages up when PHP is down covers the nginx side.
How do I know if my site was already compromised?
Patching closes the door and tells you nothing about whether someone was already inside. Patchstack’s day-one reporting, the Amazon honeypot report of an attempt on 17 October (via Tenable), and the Wiz timeline showing working WordPress code execution two months before release all mean a site that ran unpatched PHP should be checked, even if nothing looks wrong. Wiz suggests these hunting leads: unusual multipart requests followed by memory-limit errors, repeated HTTP 500 responses, oversized or malformed PHPSESSID cookies and unexplained PHP worker churn. They are leads, not proof, because a busy site produces some of them for harmless reasons. CISA also suggests watching for PHP worker processes launching shells or downloading tools.
# Memory-limit errors in the PHP error log (path varies by host)
grep -i "allowed memory size" /var/log/php*/error.log /var/log/php-fpm/*.log 2>/dev/null | tail -50

# Bursts of 500s in an nginx access log, grouped by minute
awk '$9 == 500 {print substr($4,2,17)}' /var/log/nginx/access.log | sort | uniq -c | sort -rn | head
These are our adaptation of the Wiz leads to nginx’s default combined log format, not a detection rule. If your host gives you no log access, ask for the logs from 17 to 26 October. Then check what an attacker with code execution leaves behind.
wp user list --role=administrator --fields=ID,user_login,user_email,user_registered
wp core verify-checksums
wp plugin verify-checksums --all
wp cron event list --fields=hook,next_run_relative
ls -la wp-content/mu-plugins
find wp-content/uploads -name "*.php" -print
Read the output for an administrator you did not create, a plugin that fails checksums and is not a premium plugin (premium plugins are not in the wordpress.org checksum set, so their failure is expected), a cron hook you do not recognise, and any PHP file in uploads. Our hidden admin account audit walks the same checks in more depth.
Which secrets should I rotate?
Wiz states the memory reads can expose passwords, tokens and API keys held in worker memory. A WordPress process holds the database password, the authentication keys and salts, and often payment, mail and storage keys. If you cannot rule out an earlier break-in, rotate them.
# Replace the salts in wp-config.php (logs everyone out)
wp config shuffle-salts
Change the database user’s password in the database first and in wp-config.php straight afterwards, so the site never points at a password that does not exist. Then work outward through administrator passwords, application passwords (wp user application-password list <user>), payment and mail keys, backup storage keys and deployment tokens. A rotation is finished only when nothing still uses the old key.
What has changed since the 21 October release?
As of 15 November 2026, these are the facts we could confirm and where they come from.
- Exploitation is reported. CISA put both CVEs in the KEV catalog on 26 October. Most other reports reach us through Tenable’s FAQ, last logged 28 October: an Amazon honeypot attempt on 17 October, Cloudflare’s CTO saying he was seeing early attacks on 21 October, and Trail of Bits reporting working exploits against unpatched 8.2 to 8.5. Tenable says it did not confirm one reported chained campaign. We could not read the original posts, so treat those as second-hand.
- No newer 8.x patch release exists. The php.net archive lists 8.6.0 RC7 on 12 November and nothing newer for 8.2 to 8.5.
- The NCSC-NL tracker, updated 12 November, lists 972 products: 213 fixed and 212 vulnerable, with the rest under investigation, runtime-dependent, not affected or unassessed. We did not read its full software list.
- Windows builds were rebuilt on 26 October (8.5.12-1, 8.4.27-1, 8.3.36-1, 8.2.35-1) to bundle Brotli 1.2.1 for CVE-2026-111497, a separate bug. It matters only if you host WordPress on Windows.
Common mistakes people report
These come from php-src and docker-library GitHub issues from the last four weeks, paraphrased, checked 15 November 2026.
- Trusting the Docker tag. On release day, people reported that the official php image tags for 8.3.36 and others were empty, with no published layers, until the maintainers pushed the images (“deploy glitch”). See docker-library/php issue 1702. Check the version inside the running container.
- Updating and skipping the SimpleXML regression test. Users on 8.4.27 and 8.5.12 reported
zend_mm_heap corruptedcrashes in code that touches SimpleXML objects, traced to a separate garbage collector change, not the security patch. The issue is closed and a fix was approved, but we found no release carrying it. 8.3.36 and 8.2.35 are not affected, per the docker-library note. See php-src issue 24488. Test feeds, sitemaps and import tools on staging. - Expecting hard memory limit errors to stay catchable. A reporter found that a function call that raised a normal “allowed memory size exhausted” error on 8.5.11 now kills the whole process on 8.5.12 when it crosses the new hard limit. See php-src issue 24492. If a site hits memory errors after patching, look at the process exit, not only the PHP log.
- Believing the version string. Hosts that patched by backport kept the old number, which led people to think they were exposed, and the reverse. Read the package changelog for both CVE ids.
- Forgetting the restart. Installing a package does not change a running worker. Restart PHP-FPM or Apache, then recheck from Site Health.
- Using the CLI as the proof. The shell’s PHP is often not the web server’s PHP. Use Site Health for the site.
Frequently asked questions
Do I need to update WordPress or WooCommerce?
No. The WooCommerce developer blog states that no WooCommerce or WordPress update is required or planned for these issues. Keep updating them for their own sake, but it does not address this.
Is my site safe because it is behind Cloudflare?
Not on that fact alone. The WAF rules are a stopgap and help only if the origin accepts traffic only from Cloudflare. Patch the PHP.
I updated. Do I still need a compromise check?
If the site ran an unpatched PHP between 17 October and your patch date, a quick pass is cheap and worth doing.
Is PHP 8.2 fine to stay on?
Patch to 8.2.35 now, and plan the move off 8.2 before 31 December 2026.
What we could not verify
- Who coined the name PHP2Shell. No source we read says.
- The original posts from Amazon, Cloudflare and Trail of Bits behind Tenable’s summary, and the full NCSC-NL software list.
- Whether the SimpleXML fix has shipped, beyond the fact that no new 8.x release was listed on php.net on 15 November.
- Host-by-host status today. We rely on WPVanguard’s page only for its stated 22 October snapshot.
- Any effect of the interim PHP settings. We did not test mitigations or exploits.
Sources
- php.net news archive 2026 (20, 21 and 23 October, 26 October Windows notice)
- php.net supported versions
- php-src advisory GHSA-6wmf-4rv5-p3rp and GHSA-w8hw-w9fx-j79w
- NVD CVE-2026-109619 and CVE.org CVE-2026-109618
- CISA alert, revised 26 October
- Wiz Research, PHP2Shell
- Patchstack alert (status as of 22 October)
- WooCommerce developer blog
- NCSC-NL php2shell tracker
- Tenable FAQ and watchTowr FAQ
- WordPress requirements
Plugins we build and run
We maintain these ourselves, which is why we can support them on your site.
- BuddyNextThe self-hosted community engine for WordPress
- BuddyXFree community theme, Pro when you outgrow it
- ReignPremium community theme. Add pieces, build anything
- JetonomyCommunity forum and Q&A for WordPress
- EventonomyEvents and RSVPs for WordPress communities
- LearnomyCourses and learning communities on WordPress
- ListoraDirectories and listings your members can browse
- SnipShareCode sharing built for developer communities
- WB Ad ManagerAd placements that turn traffic into revenue
- WP Career BoardA job board your community actually uses
- WP Sell ServicesSell services with offers, orders, and payouts
- MediaVersePhotos, video, and media albums for members
- WB GamificationPoints, badges, and rewards that keep members active
- Product RoadmapPublic roadmaps with voting your users trust














Related Posts

LiteSpeed Cache Vulnerability CVE-2026-93389: Check Your Version and What Was Exposed

Freemius SDK Stored XSS: How to Find Every Bundled Copy on a Client Site (Anything Under 2.13.5)
