How to Audit Your WordPress Site Security in 5 Minutes
A seven-check WordPress security audit you can run in five minutes: SSL, headers, exposed files, PHP support dates, admins, scripts and permissions.

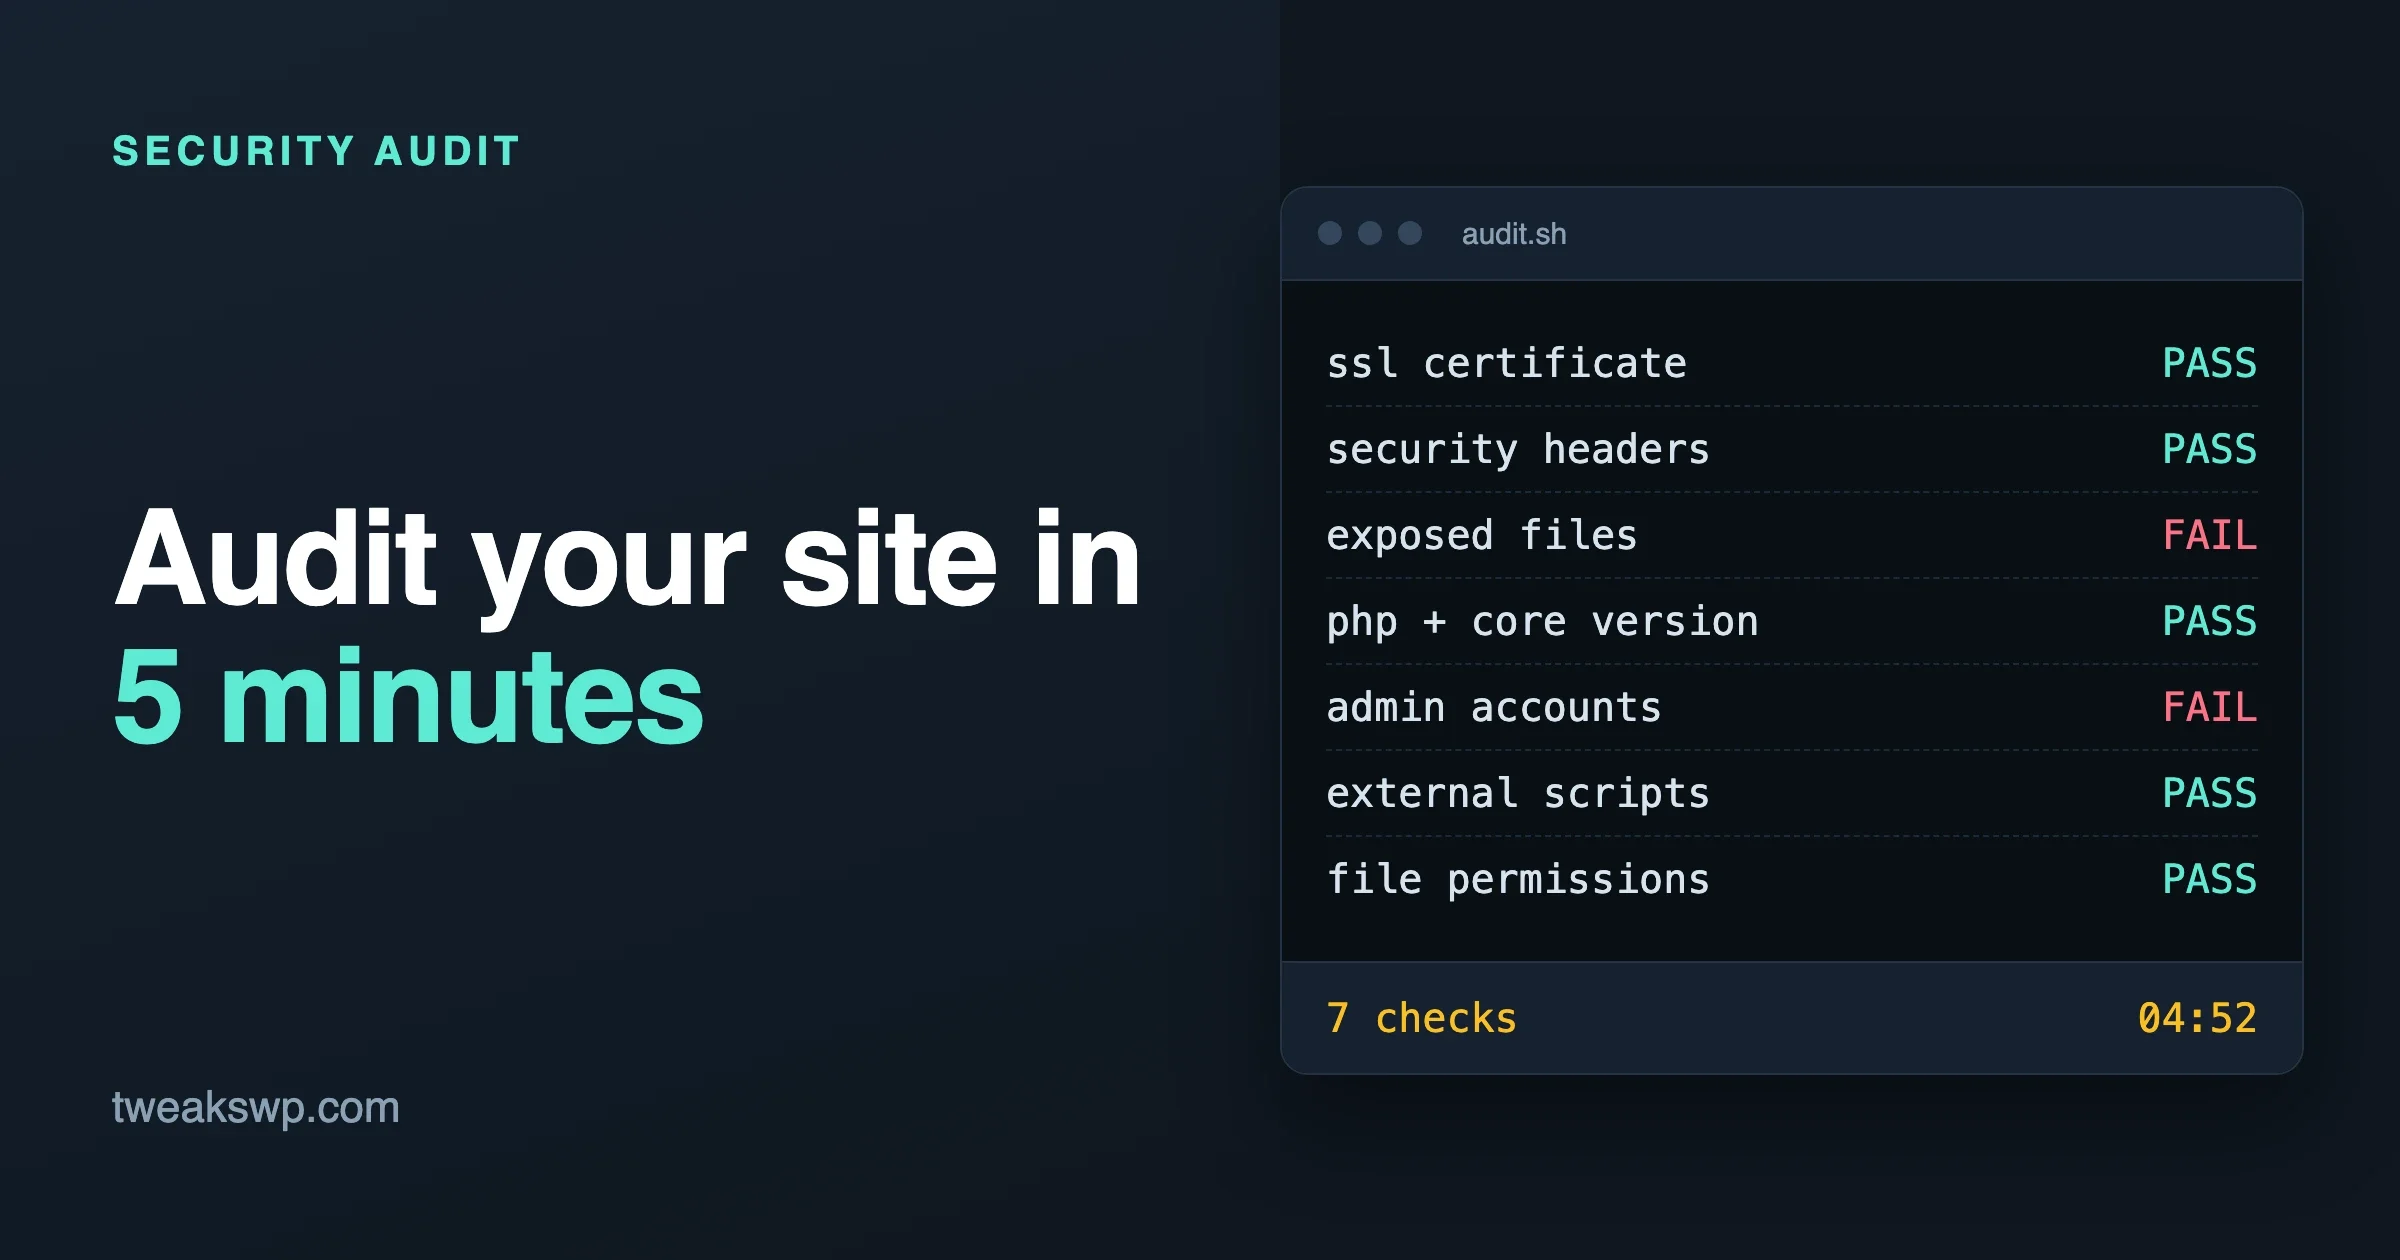
Yes, five minutes is enough to find the problems attackers actually look for. Run seven quick checks: the SSL certificate, security response headers, files that should never be public (the debug log included), PHP and WordPress versions, administrator accounts, external scripts and file permissions. Most failures on real sites are not clever holes. They are a forgotten backup file, an expired certificate, an old contractor account or a plugin nobody updated.
This is a developer-friendly audit. You need SSH or a terminal, curl, openssl and, for the account checks, WP-CLI. Every command and constant below was checked against the official WordPress documentation, the PHP release table and the WP-CLI handbook on 16 November 2026. A free scanner such as WP Vanguard covers the first few checks without a terminal, and we say exactly where it fits near the end.
An audit finds problems. It does not fix them all. At the bottom there is a table that ranks each finding by how urgent it is, so you know what to repair today and what can wait for the weekend.
The short version
- Certificate: expires in more than 30 days, matches the domain, HTTP redirects to HTTPS.
- Headers: HSTS,
X-Content-Type-Options, a framing rule, a referrer policy. Add a Content-Security-Policy in report-only mode first. - Exposed files:
debug.log,.env,wp-config.php.bakand.gitmust not return the file. A 200 means a leak. - Versions: PHP 8.1 and older are out of support. WordPress core and every plugin on the latest release.
- Accounts: every administrator is a person you can name. No open registration into a powerful role.
- External scripts: you can explain every third-party domain that serves JavaScript on your pages.
- Permissions: directories 755, files 644,
wp-config.php400 or 440 where your host allows it, file editor off.
What does a five-minute WordPress security audit actually cover?
It covers the outside view first, because that is what automated bots see. A bot does not log in. It requests a short list of URLs, reads your response headers, notes your WordPress and PHP versions, and moves on to the next domain. If your site answers that list cleanly, you have removed the cheapest attacks.
The inside view takes the remaining minutes: who can log in with what power, what code runs in your visitors’ browsers, and what the web server user is allowed to write. Here is the time budget we use.
Check | Time | Tool | What a fail looks like |
|---|---|---|---|
SSL certificate | 30 seconds |
| Expires within 30 days, wrong domain, no HTTPS redirect |
Security headers | 30 seconds |
| No HSTS, no nosniff, no framing rule |
Exposed files | 60 seconds | Shell script below | Any sensitive path answering 200 with a body |
PHP and core versions | 45 seconds | WP-CLI, host panel | PHP below 8.2, core or plugins behind |
Administrator accounts | 60 seconds | WP-CLI | An admin nobody can name, open registration |
External scripts | 45 seconds |
| A domain you do not recognise serving JavaScript |
Permissions and config | 30 seconds |
| World-writable files, file editor enabled |
A word on the figure of five minutes. It assumes you have shell access and have done this before. The first time, give it twenty. After that it is a habit you can run before every launch, after every incident and once a month on every site you look after.
How do I check my SSL certificate and HTTPS redirect?
Ask the server for its certificate and read the dates. This works from any machine and needs no login.
# checked on 16 Nov 2026
echo | openssl s_client -connect example.com:443 -servername example.com 2>/dev/null \
  | openssl x509 -noout -dates -issuer -subject

# exit code 0 = valid for at least 30 more days, 1 = expires sooner
echo | openssl s_client -connect example.com:443 -servername example.com 2>/dev/null \
  | openssl x509 -noout -checkend 2592000
The first command prints notBefore, notAfter, the issuer and the subject. The second one is the monitoring-friendly form: put it in a cron job and alert on exit code 1. For reference, our own test run against tweakswp.com on 16 November 2026 showed a certificate issued by Google Trust Services valid until 26 December 2026, which is the kind of date you want to see written down somewhere before it arrives.
Free certificates typically last 90 days (the one above ran from 27 September to 26 December), so expiry is mostly about renewal automation failing quietly. A host that renews for you can still fail when a DNS record changes or a validation path is blocked. Thirty days of warning is enough time to fix that without an outage.
Does HTTP redirect to HTTPS?
curl -sI http://example.com/ | head -5You want a 301 to the https address. If you get a 200, visitors can still load the site over plain HTTP and so can anything sitting between them and you. Fix it in the server or CDN. If your SSL terminates at a proxy, remember WordPress only sees the forwarded protocol, so a wrong setting here is a classic cause of redirect loops (we list that in the mistakes box below).
For the admin area, WordPress has a constant that forces secure sessions. The WordPress administration-over-SSL page says FORCE_SSL_ADMIN must be defined in wp-config.php and that it forces logins and admin sessions over SSL. FORCE_SSL_LOGIN was deprecated in version 4.0, so do not add it.
# checked on 16 Nov 2026
wp config set FORCE_SSL_ADMIN true --raw
Which security headers should a WordPress site send?
Send at least four: Strict-Transport-Security, X-Content-Type-Options, a framing rule and a Referrer-Policy. Add Permissions-Policy and a Content-Security-Policy as the second step. Headers cost nothing at runtime and block whole classes of browser-side attacks.
# checked on 16 Nov 2026
curl -sI https://example.com/ | grep -iE \
  'strict-transport|x-content-type|x-frame|content-security|referrer-policy|permissions-policy'
Header | What it does | A sensible starting value |
|---|---|---|
| Tells browsers to use HTTPS only for your domain |
|
| Stops the browser guessing a file type |
|
| Blocks other sites framing yours |
|
| Limits what URL data leaves your site |
|
| Turns off browser features you never use | Disable camera, microphone, geolocation and payment if unused |
| Lists where scripts, styles and frames may load from | Start with |
WordPress itself sends a framing header only on the admin and login screens, so your public pages are unprotected until you add one at the server or CDN. That is why this check belongs on the front page URL, not on wp-login.php.
Be careful with HSTS. The MDN reference explains that includeSubDomains applies the policy to every subdomain, including staging and internal tools that may not have a valid certificate. Browsers cache the policy for the full max-age, so a mistake is slow to undo. Start with a short max-age, confirm everything works, then raise it. Only add the preload directive if you have read the requirements at hstspreload.org first, because removal takes a long time.
Content-Security-Policy is the one that bites. The block editor and several admin screens rely on inline and eval-based scripts, and WordPress core has open tickets about it. Run the policy in report-only mode on a staging copy, open the editor, the media library and your checkout, and read the console errors before you enforce anything. Our full guide to security headers has working Apache and nginx snippets.
Which files must never be reachable from the web?
Backups, logs, environment files and version-control folders. If any of these returns the actual file, treat it as a breach in progress: credentials and file paths are inside. The script below checks the usual suspects and prints status, content type and size, because a 200 with a normal page body can be a soft 404 while a 200 with a tiny plain-text body is usually the real file.
#!/usr/bin/env bash
# checked on 16 Nov 2026 - run against your own site only
SITE="${1:?usage: exposed.sh https://example.com}"
for path in xmlrpc.php readme.html license.txt wp-content/debug.log .env \
            wp-config.php.bak wp-config.php.old wp-config.php~ wp-config.php.save \
            .git/HEAD wp-content/uploads/backup.zip; do
  IFS='|' read -r code type size < <(curl -s -o /dev/null --max-redirs 0 \
    -w '%{http_code}|%{content_type}|%{size_download}\n' "$SITE/$path")
  printf '%-32s %s  %-24s %s bytes\n' "$path" "$code" "${type%%;*}" "$size"
done
Read the output like this. A 404 or 403 is fine. A 301 or 302 is fine if it lands on your normal 404 page. A 200 with text/plain or application/zip on a path that should not exist is a leak. On tweakswp.com the same script printed 404 for the log and backup paths and 403 for the wp-config variants, which is what you want. (That site is not a WordPress install, so treat it as an example of clean output, not of WordPress behaviour.)
What each file leaks
Path | What an attacker gets | Fix |
|---|---|---|
| Database credentials and salts, served as plain text because PHP does not execute the extension | Delete it, rotate the database password, run |
| File paths, plugin names, stack traces, sometimes user data | Delete it, set a log path outside the web root, or deny the file |
| API keys and credentials on Bedrock-style and headless builds | Keep it above the web root; deny dotfiles |
| Your source code and its history | Do not deploy the folder; deny dotfiles |
| The WordPress version number | Low risk alone; delete or ignore |
| A remote API that allows many password guesses per request via multicall | Block it if you do not use Jetpack or the mobile app |
The WordPress debug log deserves its own sentence. WPScan’s write-up on debug log files explains that the default location and name are predictable, and that switching debugging off does not delete an existing log. Check for the file even on a site where debugging is off today. Since WordPress 5.1 you can give WP_DEBUG_LOG a custom path, which is the cleaner fix. If the log never appears at all, our guide to why debug.log is not created covers every reason.
The same goes for configuration backups. WPScan documents how a publicly reachable copy can expose database settings and secret keys, and recommends rotating keys and database passwords if one was exposed. Deleting the file is not enough once someone may have fetched it.
Blocking the leftovers on Apache and nginx
# .htaccess, above the "# BEGIN WordPress" block. Apache 2.4. Checked on 16 Nov 2026.
<FilesMatch "^(wp-config\.php\.(bak|old|save|orig)|wp-config\.php~|\.env|debug\.log)$">
    Require all denied
</FilesMatch>
RedirectMatch 404 /\.git
# inside the server block. Test with: nginx -t && nginx -s reload
location ~* /wp-config\.php.+ { deny all; }
location = /wp-content/debug.log { deny all; }
location ~ /\.(?!well-known) { deny all; }Do not block wp-config.php itself in these rules. PHP runs that file and prints nothing, and some tools request it. The danger is only in copies that the server hands out as text. If you want to block xmlrpc.php too, add a rule for that single file, but first check whether Jetpack or the WordPress mobile app is connected, since both can rely on it. Our guide on disabling XML-RPC and user enumeration covers the trade-offs.
Is my PHP, WordPress core and plugin version still supported?
Check three numbers: PHP, WordPress core and the oldest plugin. PHP is the one people forget because the host controls it. The official PHP supported versions page, read on 16 November 2026, lists these branches.
PHP branch | Released | Active support until | Security fixes until |
|---|---|---|---|
8.2 | 8 Dec 2022 | 31 Dec 2024 | 31 Dec 2026 |
8.3 | 23 Nov 2023 | 31 Dec 2025 | 31 Dec 2027 |
8.4 | 21 Nov 2024 | 31 Dec 2026 | 31 Dec 2028 |
8.5 | 20 Nov 2025 | 31 Dec 2027 | 31 Dec 2029 |
PHP 8.1 is not in that table because its security support ended on 31 December 2025, and anything older ended earlier. Treat any site on 8.1 or below as a critical finding. PHP 8.2 stops getting security fixes on 31 December 2026, which is six weeks from the day we checked, so it belongs on this month’s to-do list. WordPress.org currently recommends PHP 8.3 or newer. Test a PHP upgrade on a staging copy before your host flips the switch, because old plugins can call functions that newer versions removed.
# checked on 16 Nov 2026
wp --info | grep -i 'php version'
wp core version
wp core check-update
wp plugin list --update=available --fields=name,version,update_version
wp core verify-checksums
wp plugin verify-checksums --all
wp core verify-checksums compares your core files with the official checksums and reports any that were changed or added. wp plugin verify-checksums --all does the same for plugins, but only for plugins hosted on WordPress.org, so a premium plugin shows as not verifiable rather than clean.
Why the plugin part matters most: the Patchstack State of WordPress Security in 2026 report (page updated 25 February 2026) counted 11,334 new vulnerabilities in 2025. Of those, 91 percent were in plugins and 9 percent in themes, and only six were in WordPress core. It also reports that about half of the high-impact vulnerabilities were exploited within 24 hours. Core is rarely the weak link. An abandoned plugin usually is.
Who has administrator access to my WordPress site?
List every administrator and ask whether you can name the person and why they still need that power. This is the check most guides skip, and it is where leftover contractor accounts and quietly planted backdoor admins show up.
# checked on 16 Nov 2026
wp user list --role=administrator --fields=ID,user_login,user_email,user_registered
wp option get users_can_register
wp option get default_role
wp user application-password list 1- Unknown administrator: do not delete in a hurry. Note the registration date, compare it with any unexplained change, then follow the steps in our hidden admin account audit.
- Registration open into a strong role: if
users_can_registerreturns 1,default_roleshould besubscriberor a role you made on purpose. - Application passwords: these are API credentials that skip the login screen. List them for each administrator and revoke any you do not recognise.
- The username
admin: bots try it first. If it exists with administrator rights, create a new administrator with a strong password, log in as that user, then delete the old one and reassign its content withwp user delete admin --reassign=<new-id>.
Also check whether your REST API lists your authors. Open /wp-json/wp/v2/users in a browser. It shows public author names and slugs, which hands attackers half of a login. Login attempts are the other half, and we cover rate limiting and lockouts in our login security guide.
Which third-party scripts run on my pages?
List the external domains that serve JavaScript to your visitors, then justify each one. Every script you load from another origin runs with the full power of your page, so a compromised vendor is a compromised site.
# checked on 16 Nov 2026
curl -s https://example.com/ | grep -oE '<script[^>]+src="https?://[^"]+"' \
  | grep -oE 'https?://[^/"]+' | sort | uniq -c | sort -rn
Run it on your home page, a post, and your checkout or login page, because plugins often load different scripts per template. For each domain ask four questions: do we know what it is, does it need to load on every page, could we host it ourselves, and can it carry an integrity hash?
Subresource Integrity lets the browser refuse a file whose content changed. The MDN SRI guide describes the integrity and crossorigin attributes. You can compute a hash yourself:
# checked on 16 Nov 2026
curl -s https://cdn.example.com/lib.js | openssl dgst -sha384 -binary | openssl base64 -A
SRI only suits files that never change under the same URL, such as a pinned library version. Tag managers and analytics snippets update constantly, so a hash would break them. For those, a tight Content-Security-Policy that names the allowed domains is the better control, and an unrecognised domain in this list is worth a closer look in your theme and plugin code.
Are my file permissions and wp-config.php settings safe?
Use 755 for directories and 644 for files, keep wp-config.php readable only by you and the web server, and switch off the dashboard file editor. These numbers come from the WordPress hardening handbook page, which also says automatic updates set files to 0644 and directories to 0755.
# checked on 16 Nov 2026 - run from the WordPress root, review before running
find . -type d ! -perm 755 | head
find . -type f ! -perm 644 | head
stat -c '%a %U %n' wp-config.php   # GNU stat; on macOS use: stat -f '%Lp %Su %N' wp-config.php
wp config get DISALLOW_FILE_EDIT
The first two commands only list the exceptions, so you can read them before changing anything. The handbook says wp-config.php can also live one directory above the install, and that read access should generally be 400 or 440. Some hosts run PHP as a different user than the file owner and need 640 for that reason, so test after you change it.
# checked on 16 Nov 2026
wp config set DISALLOW_FILE_EDIT true --raw
DISALLOW_FILE_EDIT removes the plugin and theme editors from the dashboard. The handbook notes it does not stop an attacker uploading a malicious file, so it is a speed bump, not a wall. Do not confuse it with DISALLOW_FILE_MODS, which also blocks installs and updates and is a different decision. The same handbook page covers the rest of the hardening list.
If you find anything odd while you are here, rotate the salts with wp config shuffle-salts. That logs everyone out, which is the point after an incident and a nuisance on a normal day.
What should I fix first?
Fix the things that expose secrets or run attacker code first, then the things that widen exposure, then the hygiene items. This ranking is our own judgment from the findings above, not a formal scoring system.
Finding | Urgency | Why |
|---|---|---|
Readable wp-config backup.env or .git | Today, and rotate credentials | Credentials may already be copied |
Unknown administrator | Today | Possible live intrusion |
Core or plugin checksum mismatch | Today | Modified files can be a backdoor |
PHP 8.1 or older | This week | No security fixes at all |
Plugin with a known vulnerable version | This week | Mass exploitation is often fast |
Certificate under 30 days | This week | Outage risk, not a leak |
No HSTS or nosniff | This month | Hardening, low effort |
No CSP | This month, staged | Strong control, easy to break the admin |
Unrecognised external script | This week to investigate | Could be a supply chain entry |
Common mistakes people report
These come up again and again in the WordPress support forums, WPScan write-ups and core tickets. We checked each link on 16 November 2026.
- Redirect loops after forcing HTTPS. A site that terminates SSL at a proxy or on a CDN’s flexible mode can loop forever once HTTPS is forced. See the wordpress.org thread on a redirect loop after enabling HTTPS and the related force SSL redirect thread.
- HSTS with includeSubDomains on a shared domain. The policy reaches staging and internal subdomains and browsers remember it. The MDN HSTS reference describes the effect.
- A strict CSP that blanks the editor. Core ticket #50997 documents the block editor failing under a CSP that blocks eval, and #39941 tracks the long effort to allow CSP without unsafe-inline.
- Editor backup files left in the web root. WPScan’s configuration backup article shows how copies like wp-config.php.bak get served as text.
- A debug log left readable after debugging ends. See WPScan on debug log files; turning WP_DEBUG_LOG off leaves the old file behind.
- Patching core and ignoring plugins. Patchstack’s 2026 report puts 91 percent of 2025 vulnerabilities in plugins, so a clean core tells you little.
Do I need a security plugin or scanner as well?
A scanner saves typing, a plugin adds ongoing protection, and neither replaces knowing what the checks mean. Use the commands above when you have shell access and a scanner when you hand the audit to someone who does not.
We built WP Vanguard as one option for that. As of 16 November 2026 its site describes a free surface scan that needs no login and checks core, plugin and theme versions against known CVEs, security headers, SSL and exposed files such as wp-config.php.env, debug logs and .git folders, plus suspicious third-party scripts. It also lists a deep scan that looks for malware patterns, verifies core checksums and checks for rogue admins, and monitoring features that need a free account. Its page says nothing about the deep scan’s account requirement, and it shows no prices, so check both before relying on it.
The honest limits: any outside scanner sees only what the web server shows, so it cannot read your file permissions, your database or your administrator list unless it has deeper access. The terminal checks above fill that gap. A scanner also cannot judge whether a given administrator should exist. Only you can.
Frequently asked questions
How often should I audit my WordPress site security?
Monthly for a site you care about, and always after an incident, a host migration, a new developer joining or a major plugin change. The five-minute version is cheap enough to run before every launch too.
What is the quickest way to tell if my site has been hacked?
Run wp core verify-checksums and wp plugin verify-checksums --all, list administrators, and look for PHP files inside the uploads folder. A changed core file or an unknown administrator is the strongest early sign.
Is it safe to run these commands on a live site?
The read-only ones are: curl, openssl, wp user list, wp core verify-checksums. Anything that edits wp-config.php or file permissions should be tried on staging first and backed up.
Should I block xmlrpc.php?
Block it if nothing you use depends on it. Jetpack and the WordPress mobile app can rely on it, so check before you deny it. Our XML-RPC guide covers the alternatives.
Which PHP version should I be on in late 2026?
PHP 8.3 or newer. WordPress.org recommends 8.3+, 8.2 loses security support on 31 December 2026, and 8.1 is already out of support.
Does HTTPS alone make a WordPress site secure?
No. It protects data in transit and nothing else. An exposed backup file or an outdated plugin is just as dangerous over HTTPS.
Do security headers stop WordPress plugin vulnerabilities?
No. Headers limit what a browser does with your pages. A vulnerable plugin runs on the server, so you fix that by updating or removing it.
What do I do if I find a readable wp-config backup?
Delete it, change the database password, rotate the salts with wp config shuffle-salts, and check your access logs to see whether anyone requested it.
How we checked this
We ran the shell checks against tweakswp.com on 16 November 2026 to confirm the scripts run and print clean output. Facts on PHP support, the HTTPS constant, file permissions and DISALLOW_FILE_EDIT were read from php.net and the WordPress developer handbook the same day. The WP Vanguard description comes from its public site on that date. WP-CLI command names were checked against the WP-CLI handbook. We did not test the Apache and nginx snippets on a live server for this refresh, so run them on staging first.
If you would rather hand this to a team, our WordPress services team runs this audit and the fixes for client sites. It is one option among many, so compare scope and price before you pick.
Plugins we build and run
We maintain these ourselves, which is why we can support them on your site.
- BuddyNextThe self-hosted community engine for WordPress
- BuddyXFree community theme, Pro when you outgrow it
- ReignPremium community theme. Add pieces, build anything
- JetonomyCommunity forum and Q&A for WordPress
- EventonomyEvents and RSVPs for WordPress communities
- LearnomyCourses and learning communities on WordPress
- ListoraDirectories and listings your members can browse
- SnipShareCode sharing built for developer communities
- WB Ad ManagerAd placements that turn traffic into revenue
- WP Career BoardA job board your community actually uses
- WP Sell ServicesSell services with offers, orders, and payouts
- MediaVersePhotos, video, and media albums for members
- WB GamificationPoints, badges, and rewards that keep members active
- Product RoadmapPublic roadmaps with voting your users trust