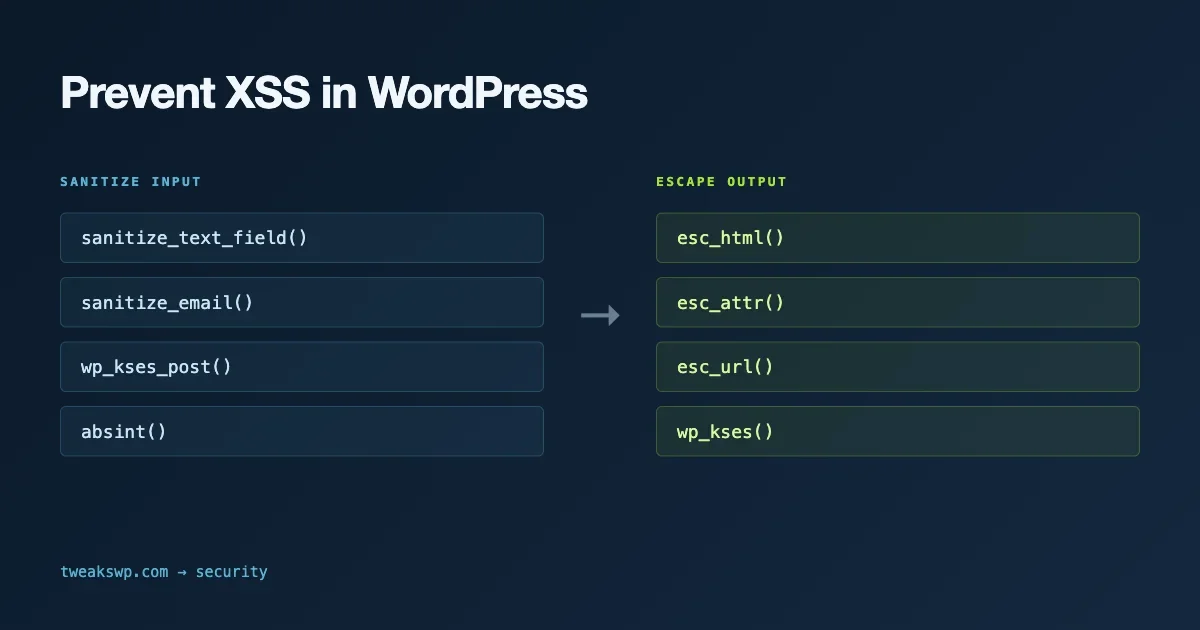
How to Prevent XSS in WordPress: Sanitization and Escaping Functions Guide
Maps every WordPress esc_*, wp_kses_*, and sanitize_* function to its exact context, with the 'sanitize on input, escape on output' rule that eliminates XSS.
How To9 min read
Maps every WordPress esc_*, wp_kses_*, and sanitize_* function to its exact context, with the 'sanitize on input, escape on output' rule that eliminates XSS.
How To9 min read
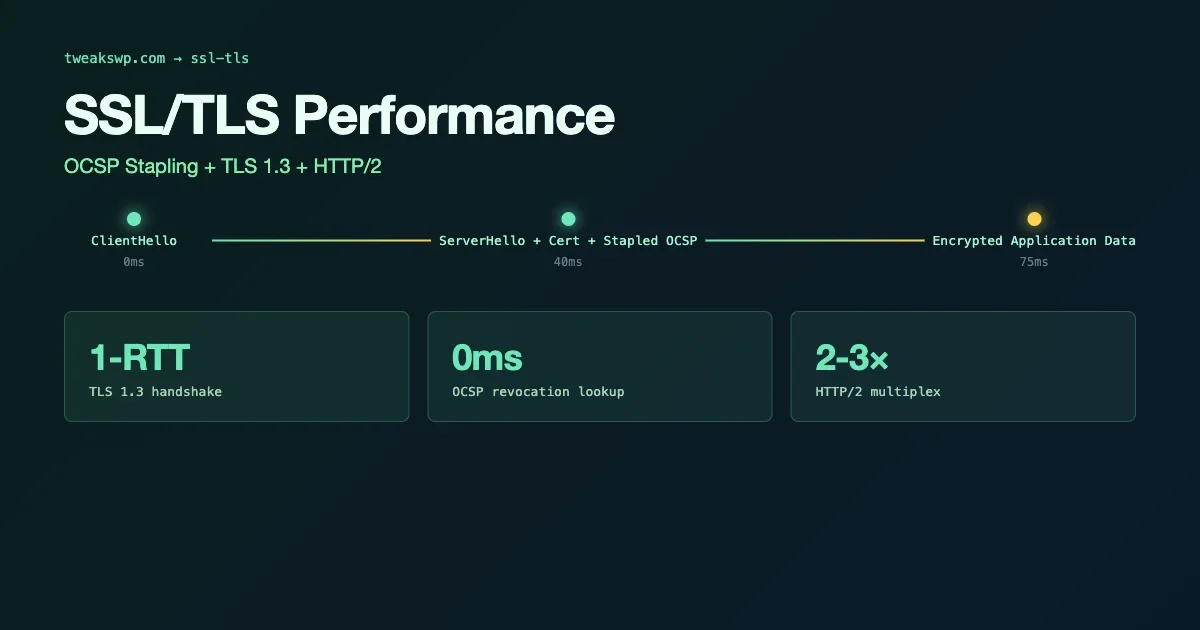
WordPress SSL/TLS performance guide covering OCSP stapling, TLS 1.3 cipher config, session resumption, HTTP/2 setup, FORCE_SSL_ADMIN, mixed content fixes, and Cloudflare Full Strict mode.
Performance7 min read
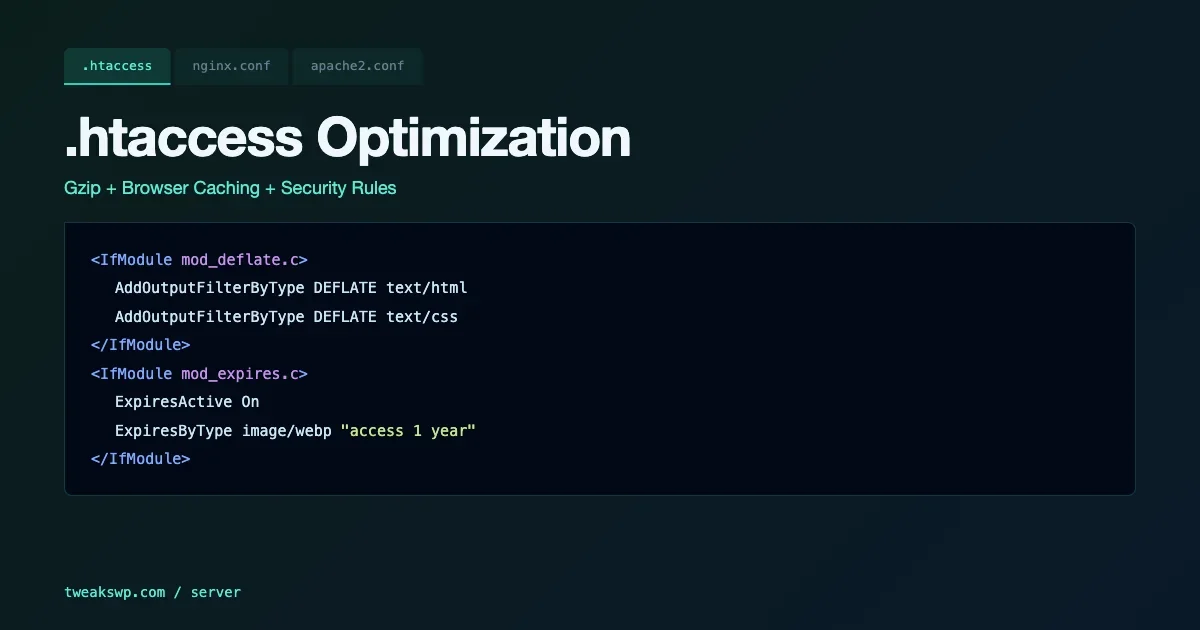
WordPress .htaccess optimization covering Gzip compression with mod_deflate, browser caching via mod_expires, ETag removal, security rules, hotlink protection, and XML-RPC blocking.
Performance7 min read
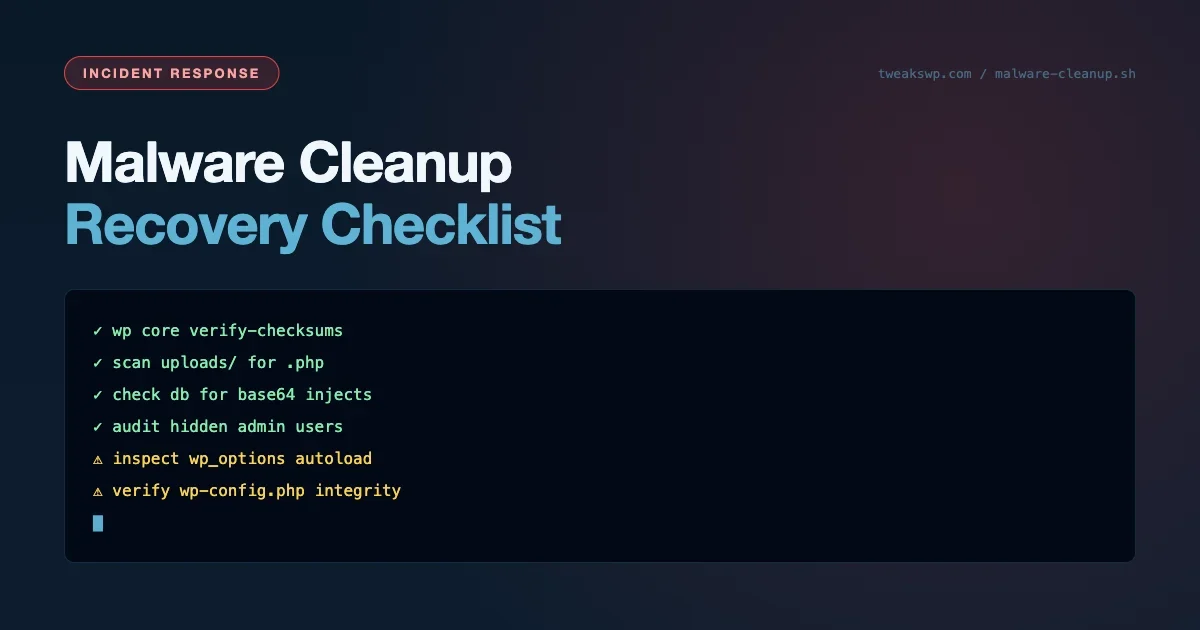
Step-by-step WordPress malware cleanup checklist covering core file verification, database injection scans, hidden admin detection, cron backdoors, and post-cleanup hardening.
How To7 min read
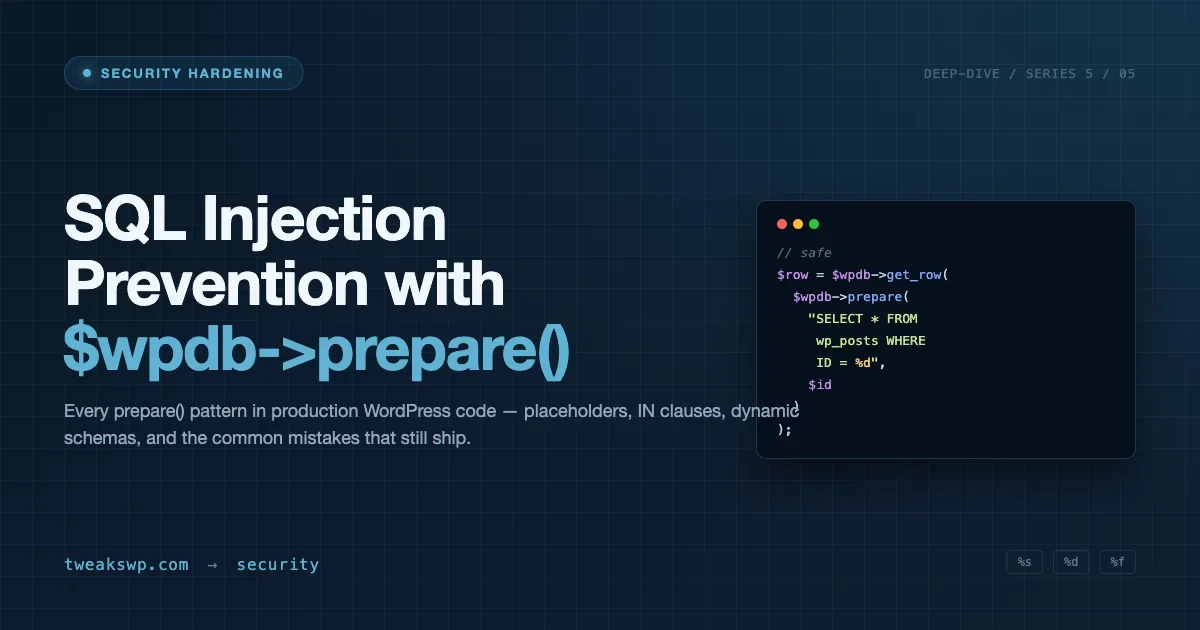
Every WordPress database query that concatenates user input without $wpdb->prepare() is a ticking time bomb. This guide covers every prepare() pattern in production code.
How To12 min read
The all-in-one WordPress community stack
Also ours: wbcomdesigns.comvapvarun.combrndle.com