How to Reduce External HTTP Requests in WordPress
How to reduce external HTTP requests in WordPress: find browser and server-side calls, cache API responses, block hosts, set timeouts, and check the result.
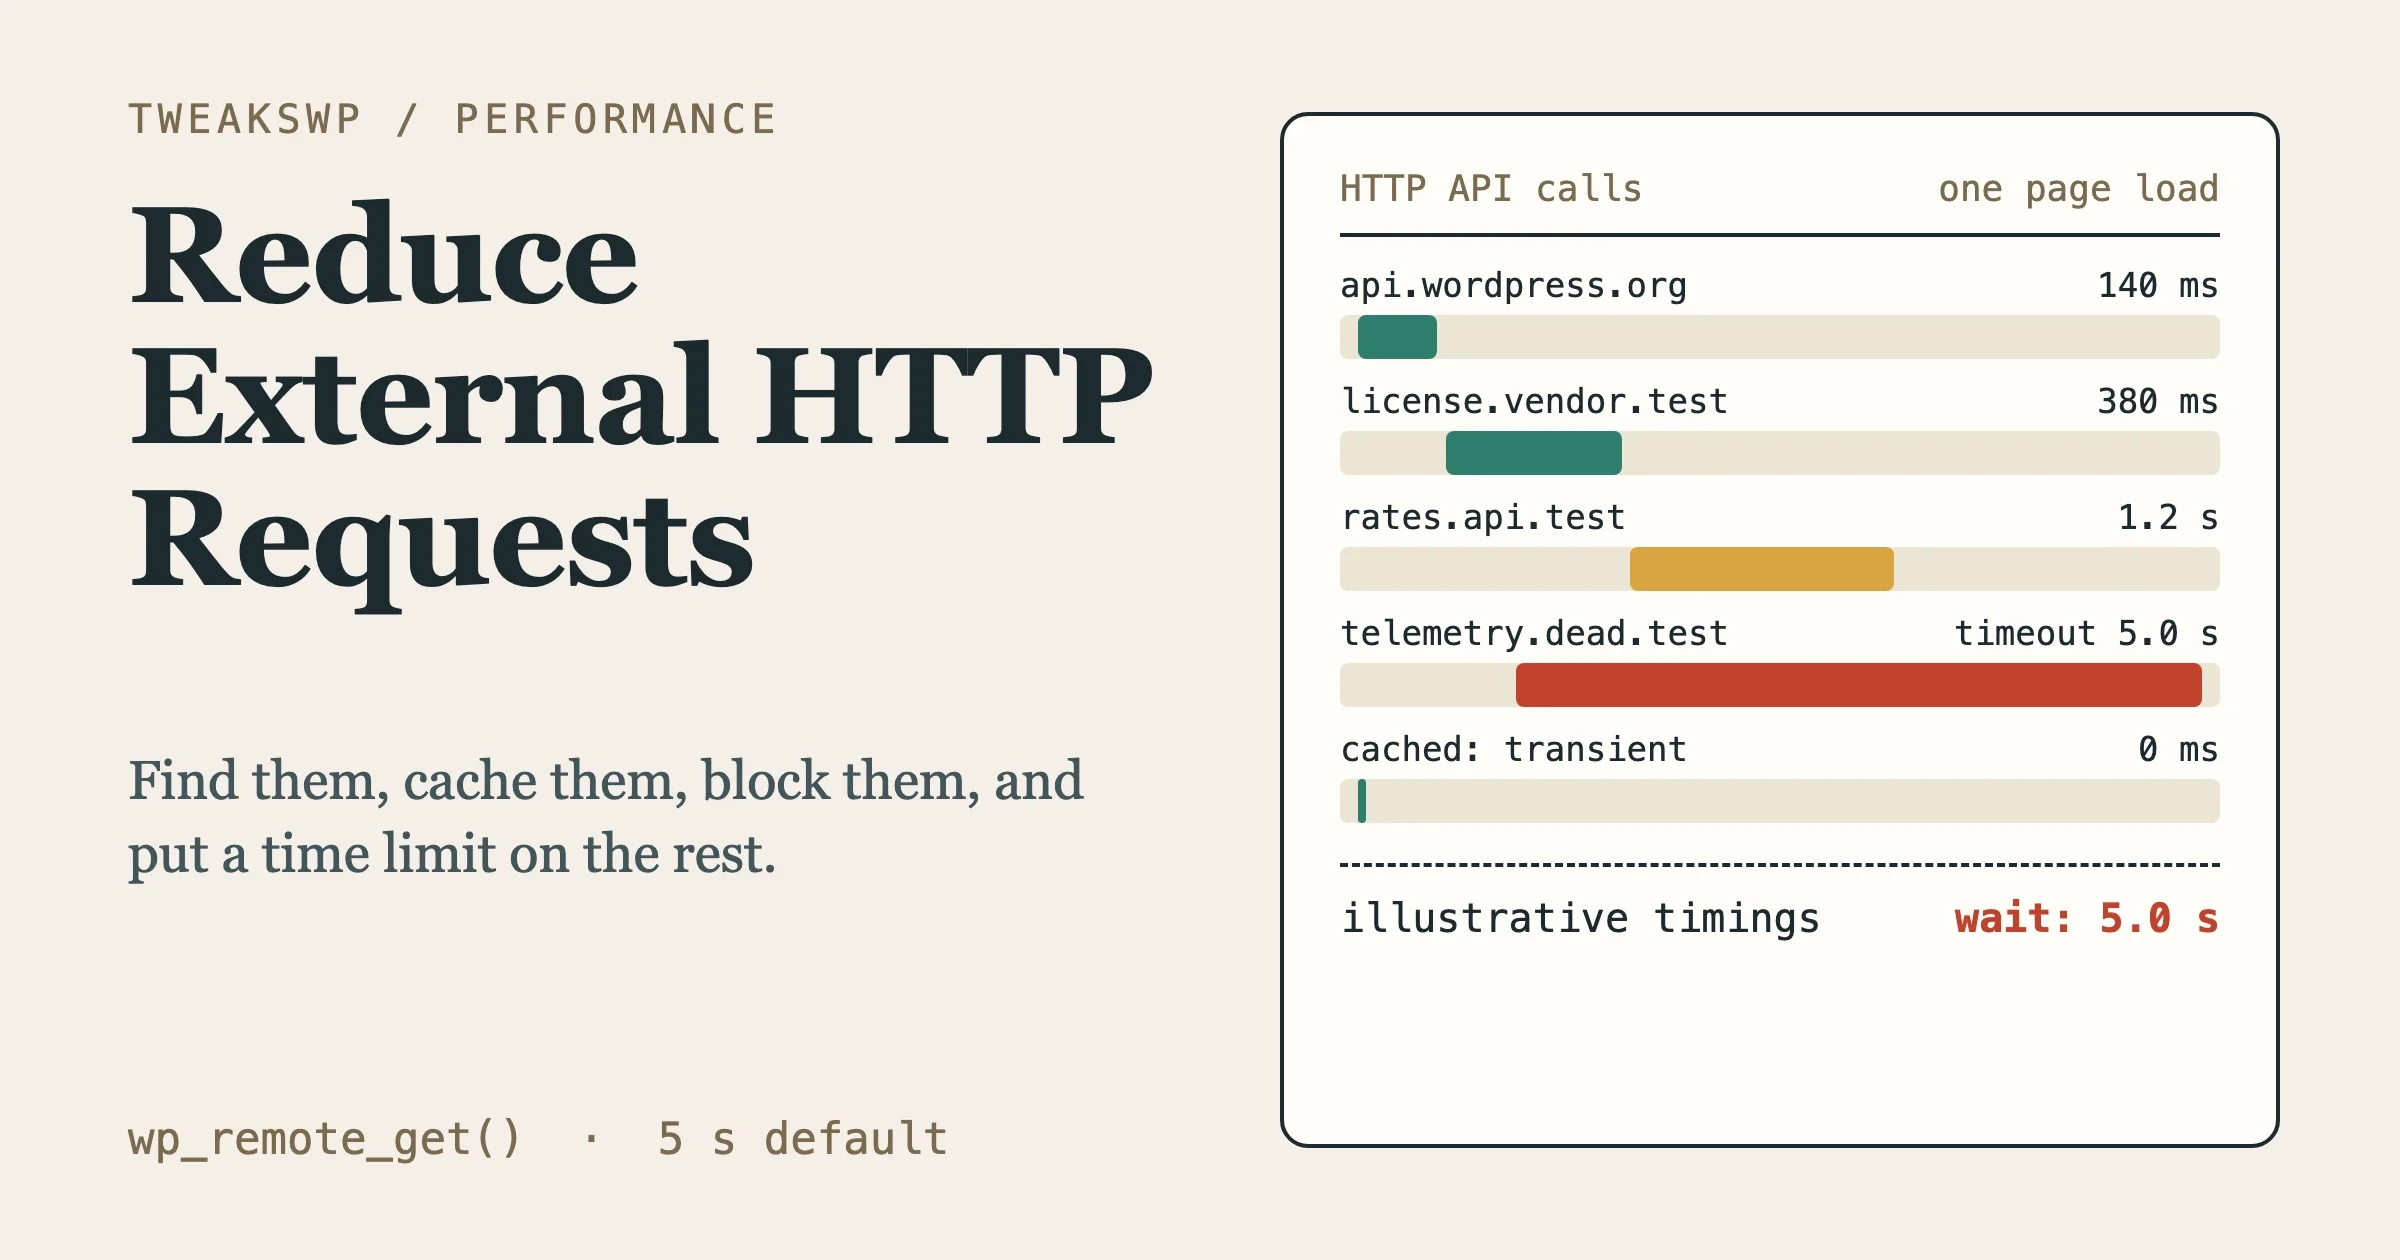
To reduce external HTTP requests in WordPress, first work out which kind you mean. Requests your visitors’ browsers make to other domains (fonts, avatars, embeds, tag scripts) are cut by removing, self-hosting or delaying those assets. Requests your server makes with wp_remote_get() and friends are cut by caching the response, blocking hosts you do not need, shortening the timeout, and moving the call out of the page request. The default timeout for the server-side kind is 5 seconds, so one dead API can hold a page for that long.
This guide does both halves, in the order we would do them on a real site: find the requests, remove the ones nobody needs, cache the ones you keep, and put a time limit on what is left. Checked on 15 Nov 2026 against the WordPress core source (trunk, 7.2 beta 5), the developer reference, Query Monitor 4.1.1 and the Chrome DevTools documentation. WordPress 7.1 is the current release line.
If your real problem is a slow first byte rather than outbound calls specifically, start with our TTFB guide. It covers server, cache and database causes, and we will not repeat them here.
Are browser requests and server requests the same thing?
No, and mixing them up is the most common reason a fix does nothing. They happen in different places and need different tools.
Browser-side (front end) | Server-side (PHP) | |
|---|---|---|
Who makes the call | The visitor’s browser | Your web server, inside PHP |
Typical examples | Google Fonts, Gravatar images, YouTube iframes, analytics tags | License checks, update checks, API data, webhooks, oEmbed discovery |
Hurts | Render time, layout shift, privacy exposure | TTFB, admin speed, PHP worker use |
Where you see it | Browser DevTools, Network tab | Query Monitor, a logger, server logs |
Main fixes | Remove, self-host, lazy-load, consent-gate | Cache, block, shorten timeout, schedule |
Covered by | No | Yes, if it goes through the HTTP API |
A Gravatar image is the classic mix-up. The <img> tag points at secure.gravatar.com, so the browser fetches it, and PHP never makes that call. Blocking external requests in wp-config.php will not touch it.
How do I find external requests in the browser?
Open the page in Chrome, open DevTools, go to the Network tab and reload. Then use the filters bar: choose More filters and tick 3rd-party requests, which per the Chrome documentation shows requests whose origin differs from the page origin. Right-click the table header and enable the Domain column, then click it to sort. Now the list reads as a count of domains instead of a wall of files.
Work through the domains in this order:
- Anything you do not recognise. Ask what feature needs it. If nobody can answer, it is a candidate for removal.
- Anything render-blocking. A stylesheet or script from another domain in the head can hold the whole page, because the browser needs a DNS lookup, a connection and a download before it can continue.
- Anything that loads on every page but is used on one. A map script on the contact page is fine. The same script on every post is not.
- Anything with a privacy cost, such as fonts, maps and embeds that tell a third party about every visitor. Sites that serve EU visitors often need consent before these load at all.
Repeat the check on a logged-out private window. Logged-in views include the admin bar and editor extras that visitors never see, and they will inflate your list.
How do I find server-side requests in WordPress?
Browser tools cannot see these. Two methods work, and we use both.
Query Monitor. The Query Monitor plugin lists HTTP API requests for each page load, with the response code, the responsible plugin or theme, and the time taken, and it flags failed requests. It has over 200,000 active installs and was last updated on 27 Oct 2026, tested up to WordPress 7.1.4 (checked on 15 Nov 2026). Install it on a staging copy if you can. Load the slow page, open the HTTP API Calls panel from the admin bar, and sort by time. Our Query Monitor tutorial walks through every panel.
Query Monitor only sees the page you load while you are logged in. It will not show the call a visitor triggers, a cron event, or a request that only fires for a certain user role. That is where a logger helps.
A temporary logger. This mu-plugin writes one line per outgoing request, with status, URL, duration, timeout and the three nearest callers. It uses the http_api_debug action, which fires after each request completes, plus a pre_http_request filter that only records the start time and never short-circuits anything.
<?php
/**
 * Plugin Name: Outgoing HTTP logger (temporary)
 */
add_filter( 'pre_http_request', function ( $pre, $args, $url ) {
	$GLOBALS['twp_http_start'][ $url ] = microtime( true );
	return $pre; // Never short-circuit here, only note the start time.
}, 1, 3 );

add_action( 'http_api_debug', function ( $response, $context, $class, $args, $url ) {
	$start  = $GLOBALS['twp_http_start'][ $url ] ?? microtime( true );
	$ms     = round( ( microtime( true ) - $start ) * 1000 );
	$status = is_wp_error( $response )
		? $response->get_error_code()
		: wp_remote_retrieve_response_code( $response );
	$caller = wp_debug_backtrace_summary( null, 4, false );
	error_log( sprintf(
		'[http] %s %s %dms timeout=%s via %s',
		$status,
		$url,
		$ms,
		$args['timeout'] ?? '?',
		implode( ' < ', array_slice( (array) $caller, 0, 3 ) )
	) );
}, 10, 5 );
Save it as wp-content/mu-plugins/http-logger.php, set WP_DEBUG_LOG to true so error_log() lands in wp-content/debug.log, load several pages, then group the log by host. If the log never appears, our guide to debug.log not being created lists every reason. Delete the mu-plugin when you are done, because it logs on every request.
One detail worth knowing: http_api_debug does not fire when a pre_http_request filter short-circuits the call. A request that another plugin answers from its own cache never shows up in this log, which is correct, because it never left your server.
Plugin-specific hosts you should expect to see: api.wordpress.org and downloads.wordpress.org (core and plugin updates), your commercial plugins’ license servers, payment and shipping APIs, and whatever analytics or CRM connectors you installed. Anything beyond that list deserves a question.
What is the default timeout for WordPress HTTP requests?
Five seconds. In WP_Http::request() the default comes from apply_filters( 'http_request_timeout', 5, $url ), and the redirect limit defaults to 5 through http_request_redirection_count. The request is synchronous, so PHP waits for the answer or the timeout, whichever comes first.
That number matters because it multiplies. Three calls to a dead host on one page can cost 15 seconds, and each held PHP worker is a worker that cannot serve anyone else. Two hooks change it, and they do not behave the same way:
http_request_timeoutsets the default value. A plugin that passes its owntimeoutargument wins over it.http_request_argsruns after the arguments are merged, so it overrides whatever the caller asked for, per URL.
For a per-host cap, use the second one:
// Checked on 15 Nov 2026 against WP_Http::request() in core trunk.
add_filter( 'http_request_args', function ( $args, $url ) {
	if ( 'api.example-analytics.com' === wp_parse_url( $url, PHP_URL_HOST ) ) {
		$args['timeout'] = 2; // Seconds. Fail fast for a non-essential host.
	}
	return $args;
}, 10, 2 );
Pick the number from the job. A tracking ping or geolocation lookup has no reason to hold a page for more than 2 seconds. A payment gateway or a bulk mail API may need longer, but those belong in a background job, not the page request. Other teams recommend similar limits: one Delicious Brains article (May 2026) suggests 1.5 seconds on busy sites, and the WordPress VIP documentation defaults its safe remote get helper to 1 second. Treat those as starting points to test on your own APIs, not rules.
How do I cache an external API response?
Use a transient with a sensible lifetime, and handle the failure case on purpose. The failure case is where most hand-rolled caches go wrong: if the API is down, a naive cache calls it again on every request and the site stays slow exactly when the API is slow.
This helper does four things. It returns a fresh cached copy when there is one, fetches with a 2 second timeout when there is not, keeps a week-long “last good” copy, and remembers a failure for a minute so a dead API is not hammered.
// Checked on 15 Nov 2026. php -l clean on PHP 8.5, behaviour tested with stubs.
function twp_cached_remote_json( string $url, int $ttl = HOUR_IN_SECONDS ): ?array {
	$key   = 'twp_http_' . md5( $url );
	$fresh = get_transient( $key );
	if ( is_array( $fresh ) ) {
		return $fresh['data']; // A fresh hit, or a remembered failure.
	}

	$stale = get_transient( $key . '_stale' );
	$res   = wp_remote_get( $url, array( 'timeout' => 2 ) );
	$data  = null;
	if ( ! is_wp_error( $res ) && 200 === wp_remote_retrieve_response_code( $res ) ) {
		$data = json_decode( wp_remote_retrieve_body( $res ), true );
	}

	if ( is_array( $data ) ) {
		set_transient( $key, array( 'data' => $data ), $ttl );
		set_transient( $key . '_stale', $data, WEEK_IN_SECONDS );
		return $data;
	}

	// Failed: serve the last good copy and do not retry for a minute.
	$fallback = is_array( $stale ) ? $stale : null;
	set_transient( $key, array( 'data' => $fallback ), MINUTE_IN_SECONDS );
	return $fallback;
}
Call it where you used to call wp_remote_get() directly. The caller gets an array or null, and the template decides what to show for null. Never let a failed lookup become a fatal error.
Choosing the lifetime is a business question more than a technical one. Ask how stale the number can be before a customer notices.
Data | Reasonable cache time | Why |
|---|---|---|
Plugin license status | 12 to 24 hours | Rarely changes, a failed check should not lock anything |
Exchange rates, shipping estimates | 30 to 60 minutes | Moves slowly, wrong by a small amount is tolerable |
RSS or social feed | 1 to 6 hours | Nobody expects second-level freshness |
Weather, stock levels | 5 to 30 minutes | Depends on how much a stale value costs you |
Anything tied to one user or an order | Do not share across users | Key it per user, or do not cache it |
Where the data lives matters too. Without a persistent object cache, transients are stored as rows in wp_options, which means a database read on every hit. With Redis or Memcached, the same calls are served from memory. Our guide on finding and deleting expired transients covers what an unmanaged transient table looks like, which is worth reading before you add a few hundred cache keys of your own.
Invalidation is the other half. When you know the data changed, call delete_transient() on the matching key. When the remote service offers a webhook, delete the key from the webhook handler. When neither is possible, a shorter lifetime is the honest answer.
How do I block external requests with WP_HTTP_BLOCK_EXTERNAL?
Define the constant in wp-config.php. It blocks every request made through the WordPress HTTP API except requests to localhost and to your own site’s host. WP_ACCESSIBLE_HOSTS is a comma-separated allowlist of hosts that may still be called.
// Staging: nothing leaves the server except WordPress updates.
define( 'WP_HTTP_BLOCK_EXTERNAL', true );
define( 'WP_ACCESSIBLE_HOSTS', 'api.wordpress.org,downloads.wordpress.org' );
Checked on 15 Nov 2026 against WP_Http::block_request() in core trunk. A few details the manual page does not make obvious:
- A blocked request returns a
WP_Errorwith the codehttp_request_not_executedand the message “User has blocked requests through HTTP to the URL”. There is no network wait, so nothing times out. - Wildcards work:
*.wordpress.orgallows every subdomain. The wildcard is turned into the pattern.+, so it needs something in front of the dot. It matchesapi.wordpress.organd does not match barewordpress.org. List the bare host as well if you need it. - Requests to your own site and to
localhostare allowed by default. Theblock_local_requestsfilter changes that. - Plugins that call
curl_exec(),file_get_contents()orfsockopen()directly skip all of this. The constant only governs the WordPress HTTP API. - It is a site-wide switch set at boot. You cannot use it to block one plugin. For that, use a filter.
Where we would use it: staging and development copies, so a cloned site does not send emails, charge cards, run license checks against production keys or report your staging URL to a vendor. Where we would not: a production store that takes payments, runs updates through the dashboard and uses a CRM connector, unless you have the full list of hosts and have tested each feature.
How do I stop one slow host without blocking everything?
Return an answer from pre_http_request. The filter runs before the request is sent, and per the core source, returning anything other than false skips the request and uses your value as the response. A WP_Error is a valid return value, and so is a response array with headers, body, response, cookies and filename keys.
// Checked on 15 Nov 2026 against WP_Http::request() in core trunk.
add_filter( 'pre_http_request', function ( $pre, $args, $url ) {
	if ( 'telemetry.example.com' === wp_parse_url( $url, PHP_URL_HOST ) ) {
		return new WP_Error( 'blocked_by_site', 'Telemetry call blocked.' );
	}
	return $pre; // Pass the incoming value on so other filters still work.
}, 10, 3 );
Two notes. Return $pre rather than a literal false, so you do not undo another filter’s answer. And because pre_http_request runs before the WP_HTTP_BLOCK_EXTERNAL check, a filter that answers for a blocked host will bypass the block. That is rarely what you want, so keep the two mechanisms separate in your head: the constant is a wall, the filter is a per-request decision.
Before you block a call from a plugin, check what the plugin does when it gets an error. A well-written plugin treats a WP_Error as “no data” and carries on. A careless one assumes an array and throws a warning. Test the page and the admin after you add the filter, with debug logging on.
How do I move a request off the page load?
If nobody needs the result before the page renders, do not make the visitor wait for it. Schedule a single WP-Cron event, return immediately, and let the HTTP call happen on a later request.
// Checked on 15 Nov 2026 against wp_schedule_single_event() in core trunk.
add_action( 'twp_send_event', function ( array $payload ) {
	wp_remote_post( 'https://analytics.example.com/collect', array(
		'timeout' => 5,
		'body'    => $payload,
	) );
} );

// In the code that used to make the call inline:
wp_schedule_single_event( time(), 'twp_send_event', array( $payload ) );
This suits webhooks, analytics events, CRM sync and activity logs. It does not suit anything the response depends on, such as a payment authorisation or a shipping quote at checkout.
Know the limits before you rely on it:
wp_schedule_single_event()ignores an event that is identical (same hook and same arguments) to one already scheduled within 10 minutes. Include a unique value in the arguments, such as an event ID, if each call must run.- Standard WP-Cron is triggered by page visits. On a quiet site the job can sit waiting. A real server cron that calls
wp-cron.php, withDISABLE_WP_CRONset to true, fixes that. Our guide on monitoring WP-Cron and Action Scheduler failures shows how to know when a job did not run. - For a high volume of jobs, a queue such as Action Scheduler retries and logs better than raw cron events.
Which external requests does WordPress itself make?
Most of core’s outbound traffic is not on the page-render path, which is why it usually is not the first thing to fix. This table separates what core does from what plugins do. Core behaviour was checked in the source on 15 Nov 2026.
Request | Side | When it happens | What you can do |
|---|---|---|---|
Core, plugin and theme update checks | Server | Twice-daily cron events, plus admin screens once the stored result is older than about 12 hours (about 1 hour on the Plugins screen) | Leave it. Keep |
oEmbed discovery and fetch | Server | When a post with an embed URL first renders | Cache holds for a day by default ( |
WP-Cron spawn | Server | After a page load when jobs are due, a loopback request with a 0.01 second timeout | Use a real server cron on busy or quiet sites |
Gravatar images | Browser | Every comment or avatar shown | Turn off Show Avatars, or filter |
Fonts from Google | Browser | Theme or plugin enqueues | Self-host the font files |
YouTube, X and similar embeds | Browser | Iframe or script on each page that has one | Lazy-load, or replace with a click-to-load preview |
Plugin license and telemetry calls | Server | Varies by plugin, often on every admin load | Cache, filter or ask the vendor |
On oEmbed, a correction to what many older guides say: WordPress stores oEmbed results in post meta keys that start with _oembed_, with a oembed_cache post type as a fallback, not in an option. If an embed looks slow on the first view and fast on the second, that is the cache warming up.
How do I cut third-party requests on the front end?
Go domain by domain from your DevTools list, and apply the smallest fix that works.
Fonts. Loading a Google Font from fonts.googleapis.com costs a DNS lookup and a connection to one host, then another to fonts.gstatic.com for the files. Hosting the files on your own domain removes both. On a block theme running WordPress 6.5 or later, the built-in Font Library can install a Google Font into your site’s font directory, so visitors’ browsers load it from your domain. Otherwise download the WOFF2 files and declare them with @font-face and font-display: swap. Then confirm in the Network tab that no request to either Google host remains. A child theme or plugin that still enqueues the old stylesheet is the usual leftover.
Avatars. Settings, then Discussion, has a Show Avatars switch. Core checks the show_avatars option before it builds an avatar unless a caller forces display. On a site with comments or member lists, turning avatars off removes a whole domain. If you want avatars, filter pre_get_avatar_data to return a local URL for users who uploaded one. Our guide on Gravatar not changing explains how the hash and caching work.
Embeds. A video iframe loads a lot of third-party code before anyone presses play. Replace the iframe with a preview image and load the real player on click. A plugin does this for you, or you can hand-roll it for one or two videos.
Scripts and tags. Every tag manager container is a door to more requests, because tags can load further tags. Audit the container, remove dead tags, and load the rest after interaction or consent where the law and your analytics needs allow it.
Preconnect, last. A preconnect or dns-prefetch hint warms the connection to a host you cannot avoid. Add one for a host that is critical and early. Do not add them for everything, because each hint costs a connection.
What common mistakes do people report?
These come from forum threads, vendor guides and plugin documentation. We paraphrased each one, linked the source, and checked the links on 15 Nov 2026.
- Blocking external requests and then losing a feature. One SiteGround user set the block with an allowlist for
*.wordpress.organd two hosting domains, then found a PHP version switch failing. A request-monitoring plugin showed it was calling a host nobody had listed, and adding it fixed it (wordpress.org support thread, February 2020). Lesson: log the hosts first, then build the allowlist. - Assuming the block covers everything. The documentation of a request-manager plugin states that it only detects requests made through the WordPress HTTP class, and not direct
curl_exec(),fsockopen()orfile_get_contents()calls (HTTP Requests Manager). The same limit applies to the core constants. - A plugin that calls out on every admin page. A site owner found a slow
wp_remote_get()request on every dashboard page and traced it to a consent plugin’s cookie scan. The vendor’s answer was to let the scan finish, switch it off, or define a constant to skip it (wordpress.org support thread, September 2023). Check each plugin’s settings before you write a filter. - Calling an API with no fallback. The WordPress VIP documentation says uncached remote requests should never run on the front end, and describes helpers that return a fallback value after repeated failures (WordPress VIP, updated December 2025). A cache with no failure path is the same mistake in a different shape.
- Long waits that use up PHP workers. A May 2026 article describes how a slow API call can occupy the worker pool and cause 502 or 504 errors even on pages that do not call the API, and how a short lock and a circuit breaker limit the damage (Delicious Brains). Short timeouts are a stability setting, not only a speed setting.
How do I check that it worked?
Measure before and after on the same page, with the same logged-in state.
- Server-side count. Load the page with Query Monitor open and note how many HTTP API calls it lists and the total time. After caching, a repeat load should show none for the calls you cached.
- Browser-side count. In DevTools with 3rd-party requests ticked, note the number of third-party requests and the domains. The count of domains is the number to reduce.
- First byte. Compare the document request’s Waiting for server response time in the Network tab. If outbound calls were the cause, this is where the change shows up.
- Failure test. Block the host in your hosts file or with the
pre_http_requestfilter on a staging copy, and reload. The page should still render, with a fallback, in roughly normal time. This is the test most teams skip, and it is the one that proves the work. - Admin test. Open the dashboard, the plugins screen and an edit screen. Admin pages are where license checks live.
A caveat on expectations: removing or caching an external call only helps if that call was slow or blocking. A fast, reliable API that runs once an hour costs you nothing, and no setting will make the page meaningfully faster by touching it. Start with the calls that sit on the critical path and have the worst timing in your log.
When should you leave external requests alone?
Update checks, payment gateways, shipping quotes at checkout and authentication providers exist because the site needs them. Blocking them breaks something. For those, the goal is to keep them reliable: sensible timeouts, a fallback, and no repeat calls inside one request. If your goal is outright zero third-party requests for privacy reasons, that is a different project with its own trade-offs, and you should write down each feature you give up.
Frequently asked questions
Does blocking external requests break plugins?
It can. A plugin that needs its vendor’s server for licensing, updates or data returns an error when blocked. Many handle it quietly and a few do not. Allowlist the hosts you need, test the features, and keep the block for staging unless you have verified production.
What is the difference between wp_remote_get and file_get_contents?
wp_remote_get() goes through the WordPress HTTP API. That means it respects WP_HTTP_BLOCK_EXTERNAL, passes through pre_http_request and http_request_args, appears in Query Monitor and the logger above, and returns a WP_Error you can check with is_wp_error(). file_get_contents() on a URL bypasses all of that. For code that talks to a remote URL inside WordPress, use the HTTP API. For URLs that come from user input, use wp_safe_remote_get(), which rejects unsafe destinations.
Where is the 5 second timeout set?
In WP_Http::request(), as the default for the timeout argument, filtered by http_request_timeout. A caller can pass its own value, and the http_request_args filter can override it afterwards.
Can I allow only some hosts?
Yes. Set WP_HTTP_BLOCK_EXTERNAL to true and list the hosts you want in WP_ACCESSIBLE_HOSTS, separated by commas. Wildcards like *.wordpress.org are supported and match subdomains only.
Do transients work for this without Redis?
Yes. Without a persistent object cache they live in wp_options, which costs a database read per hit but still saves the network call. With Redis or Memcached they are served from memory. In both cases set a lifetime and plan for the failure case.
How often does WordPress check for updates?
Core, plugin and theme checks are scheduled twice daily, and admin screens refresh a stored result once it is older than about 12 hours, with shorter windows on update-related screens. These calls run in the background or in the admin, not in front-end rendering. We would leave them alone.
How do I know which plugin makes a request?
Query Monitor shows the responsible component for each HTTP API call. The logger above prints the nearest callers, which usually include the plugin folder name in the file path.
What to do next
Run the logger on staging for a day, run the DevTools check on your three busiest templates, and write down every external host with a reason it exists. Cache or schedule the server-side calls that sit on the page path, self-host what you can on the front end, and put a short timeout on anything left. Add a block on staging so a cloned site stays quiet. For the wider performance picture, our wp-config.php constants reference covers the other switches worth knowing, and the TTFB guide covers what to check once outbound calls are no longer the cause.
Plugins we build and run
We maintain these ourselves, which is why we can support them on your site.
- BuddyNextThe self-hosted community engine for WordPress
- BuddyXFree community theme, Pro when you outgrow it
- ReignPremium community theme. Add pieces, build anything
- JetonomyCommunity forum and Q&A for WordPress
- EventonomyEvents and RSVPs for WordPress communities
- LearnomyCourses and learning communities on WordPress
- ListoraDirectories and listings your members can browse
- SnipShareCode sharing built for developer communities
- WB Ad ManagerAd placements that turn traffic into revenue
- WP Career BoardA job board your community actually uses
- WP Sell ServicesSell services with offers, orders, and payouts
- MediaVersePhotos, video, and media albums for members
- WB GamificationPoints, badges, and rewards that keep members active
- Product RoadmapPublic roadmaps with voting your users trust














Related Posts

LiteSpeed Cache Vulnerability CVE-2026-93389: Check Your Version and What Was Exposed

Freemius SDK Stored XSS: How to Find Every Bundled Copy on a Client Site (Anything Under 2.13.5)
